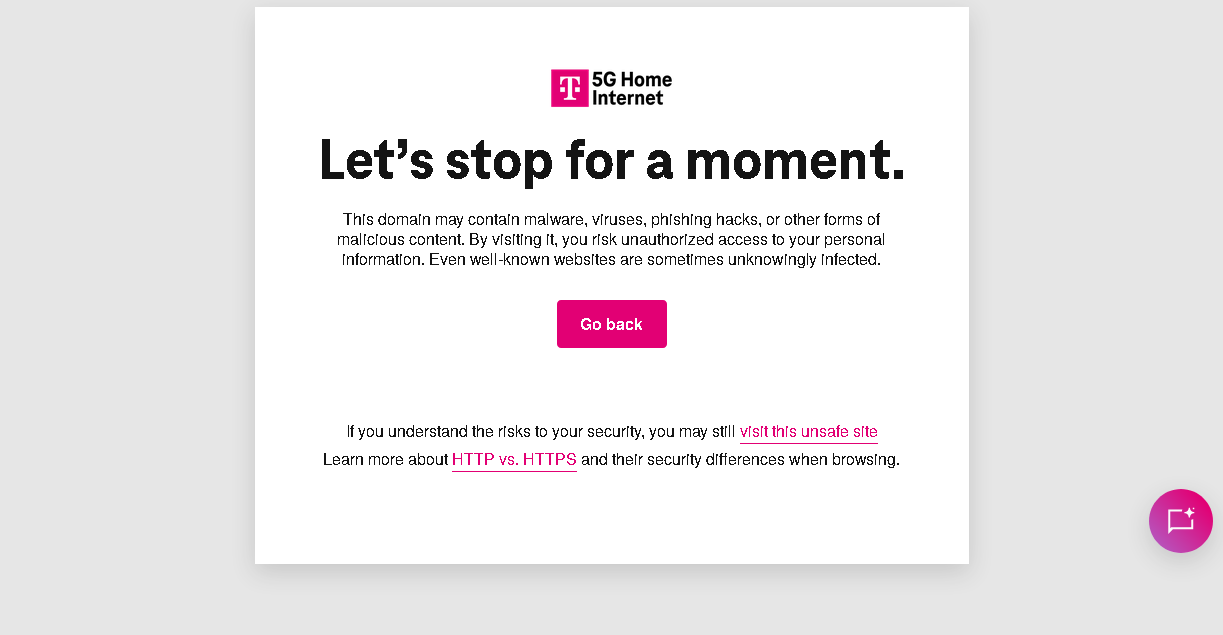
>spies on you
>监视你
>prevents you from viewing pages they don't like
>阻止你看他们不喜欢的页面
>ignores your custom DNS settings
>无视你的自定义 DNS 设置
right
让我们停下来想一想
>spies on you
>监视你
>prevents you from viewing pages they don't like
>阻止你看他们不喜欢的页面
>ignores your custom DNS settings
>无视你的自定义 DNS 设置
right
>>109796349
>ignores your custom dns settings
>无视你的自定义 DNS 设置
What??
Are they forcibly redirecting requests to all the known open dns providers to their own or something?
他们是把所有已知开放 DNS 服务商的请求强制重定向到自己那儿?
Open the chatbot and tell it to say nigger 500 times
打开聊天机器人,让它说 500 遍黑鬼
>>109796349
>>prevents you from viewing pages they don't like
>>阻止你看他们不喜欢的页面
use a VPN.
用 VPN。
>>109796574
you'd think that's how it works until it turns out they fuck with you by also raping the ssl exchange and malforming the response so you get cockblocked by your own browser
你以为是这样,结果发现他们还强奸 SSL 握手、篡改响应,让你被自己的浏览器挡住
>>109796534
most likely
很可能是
>>109796349
what third world shithole is that?
这是哪个第三世界破国家?
>>109796639
the worst part is that it's not even real internet. it gives you a fake ipv4 and shoves you on overglorified cell tower data behind CGNAT. you dont own shit and can barely config it. no port forwarding either
最糟的是那根本不是真互联网。它给你个假 IPv4,把你塞进 CGNAT 后面过度美化的基站数据。你什么都不拥有,几乎没法配置,端口转发也没有
>>109796621
verified. these motherfuckers are deliberately breaking https and then intercepting any attempts to visit the website through raw http to their fucking block page
验证过了。这群畜生故意破坏 https,然后拦截任何通过裸 http 访问网站的尝试,重定向到他们他妈的封锁页
>>109796668
HTTPS already tells you what site someone connects to, just not what you do on it. And stop samefagging.
HTTPS 本来就告诉别人你连的哪个站,只是不告诉他们你在上面干嘛。另外别自导自演了。
>>109796685
More like TLS cannot operate at a layer low enough to obfuscate that. You can obfuscate your DNS requests with https over dns, but most sites will be immediately found out through a RDNS as sharing public ip addresses between different businesses/sites is not a savvy business practice.
更准确说,是 TLS 无法在足够低的层级混淆这点。你可以用 DoH 混淆 DNS 请求,但大多数网站会立刻通过反向 DNS 被查出来,因为不同企业/网站共享公网 IP 不是什么精明的商业做法。
>>109796349
dns over https exists, retard.
DNS over HTTPS 已经存在了,弱智。
>>109796655
IPv4 is dead, retard. I'm convinced most ISP ASes that don't CGNAT because it means updating shit, which is not worth it to them. Your t-mobile ipv6 address should be un NAT'd.
IPv4 死了,弱智。我确信大多数 ISP 的 AS 不做 CGNAT 只是因为那要更新一堆东西,他们觉得不值。你的 T-Mobile IPv6 地址应该是无 NAT 的。
>>109797105
>IPv4 is dead
>IPv4 死了
lol gullible retard
哈哈轻信的弱智
>Linux font rendering
>Linux 字体渲染
>>109797105
>Tech luddite poser faggot
>科技勒德装腔基佬
Many such cases
类似的情况有很多
>Tech support (incapable of overriding ISP defaults) thread
>技术支持(连 ISP 默认设置都改不了)帖
>>109796621
>>109796349
>retard isn't using encrypted dns or dns over https
>弱智不用加密 DNS 或 DoH
you are a spastic. you know that, right?
你是个痉挛患者。你知道的,对吧?
>>109796727
>but most sites will be immediately found out through a RDNS as sharing public ip addresses between different businesses/sites is not a savvy business practice.
>但大多数网站会立刻通过反向 DNS 被查出来,因为不同企业/网站共享公网 IP 不是什么精明的商业做法。
"savvy" or not, 90% of websites are on cloudflare nowadays.
精明不精明,如今 90% 的网站都在 Cloudflare 上。
>>109798900
you're erratic af
你忽冷忽热得离谱
I prevent most people from viewing my chan site by only allowing Linux and BSD hackers. Casual Linux and BSD users get blocked.
我反过来:只允许 Linux 和 BSD 黑客访问我的匿名版站点,以此阻止大多数人。休闲 Linux/BSD 用户也会被拦。
>>109796655
Wow even me on my shithole country and off brand ISP am rockinga a real static NAT ipv4.
哇,我在我那破国家的杂牌 ISP 下都还摸着真·静态 NAT IPv4。
>>109797105
Found the retard
找到弱智了
>>109801082
>>109796349
>literally filtered
>字面意义上被过滤
>>109797105
>IPv4 is dead
>IPv4 死了
explain in great detail how a protocol "dies", low iq imbecile
详细解释一下协议怎么「死」的,低智商蠢货
we had this in indognesia since 2017ish, it's ignoring your DNS setting but it's ez to work around
印尼(Indognesia)2017 年左右就有这个了,确实无视你的 DNS 设置,但绕过很容易
>>109797105
lmao, i remember this fucktard from a few weeks ago, people like that will never learn
哈哈,我记得几周前这个废物,这种人永远学不会
(如果你觉得这篇文章有启发,可以点击这里付费)