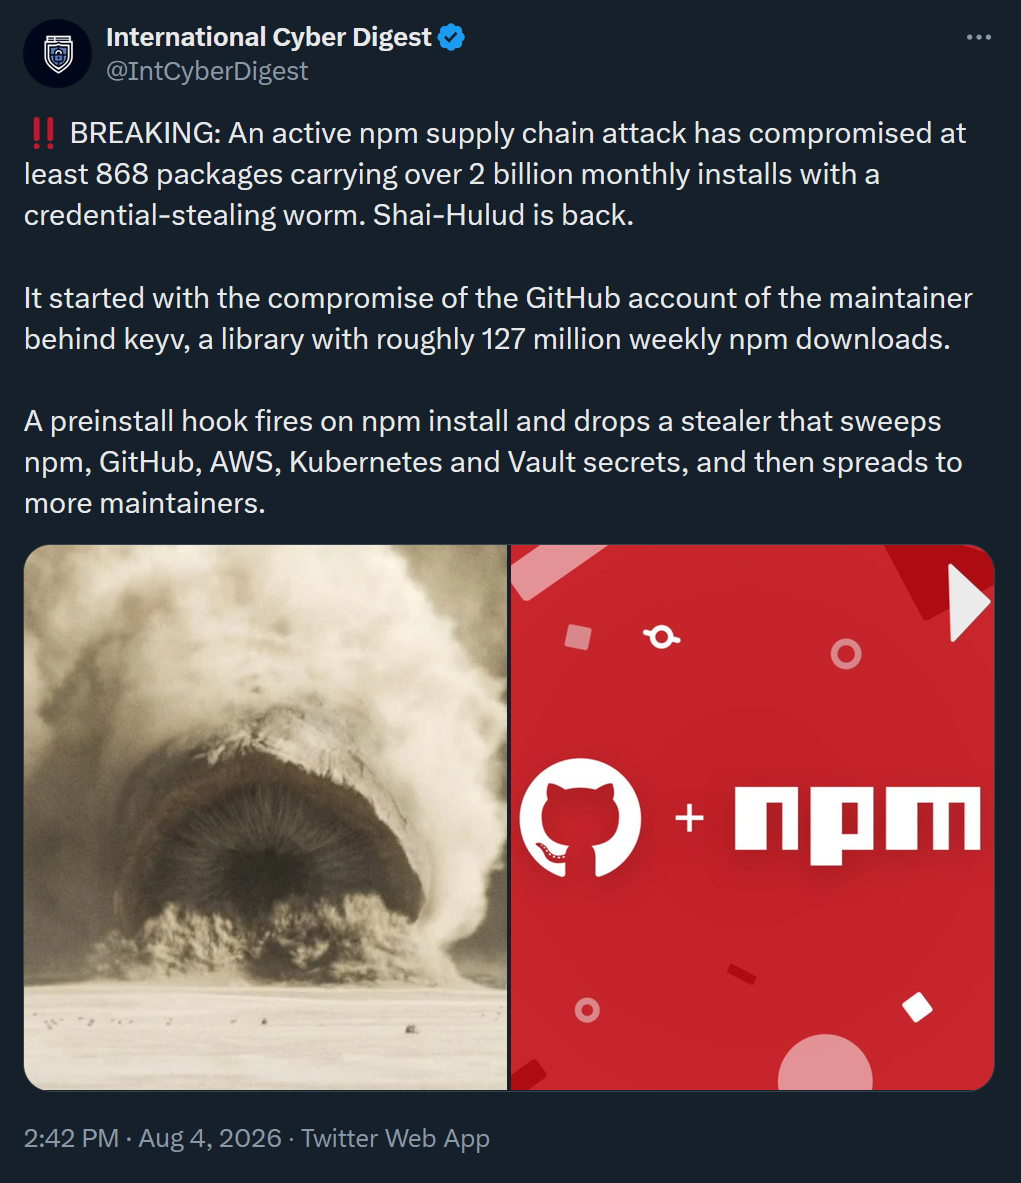
It's tuesday, so shai hulud is back and packages with ~2bn/mo installs have been compromised again
又到周二了,沙虫又回来了,月安装量约20亿的包又被搞了
https://www.aikido.dev/blog/keyv-and-friends-compromised-in-npm-supply-chain-attack
npm供应链攻击。
It's tuesday, so shai hulud is back and packages with ~2bn/mo installs have been compromised again
又到周二了,沙虫又回来了,月安装量约20亿的包又被搞了
https://www.aikido.dev/blog/keyv-and-friends-compromised-in-npm-supply-chain-attack
Why don't they just have AI scanning each upload for malware?
他们为什么不用AI扫描每个上传的包来查恶意软件?
>>109458879
so I assume this is a nothing burger cause the "major organizations" they mention are literal whos. no large framework affected as it appears.
所以我猜这就是个没卵事,因为他们提到的“主要机构”全是无名小卒。看起来没有大型框架受影响。
UPDOOTERS BTFO ONCE AGAIN
>>109459513
It probably complex, the scripts are supposed to do many things and node developers are known run cross dependencies on a one liner projects to 100k line project
这可能挺复杂的,脚本要干很多事,而且Node开发者出名地喜欢在一行项目的依赖上跨来跨去,从100行到10万行项目都这样。
In rust, this is just cargo add shai-hulud.
在Rust里,这就只是cargo add shai-hulud。
>>109458879
That's why i would never touch something as pozzed as node.js or Python.
这就是为什么我永远不会碰node.js或Python这种被污染的东西。
How many more times will this happen until they figure out a better way for distribution
到底还要发生多少次他们才能想出更好的分发方式?
node trannies, not like this
node那群人,别这样搞啊
not like this
不该是这样
>>109458879
>Heh I'll call this shai hulud because that's dope, >hackerman and sci-fi. Just like me!
>嘿,我要叫它沙虫,因为这太酷了,>黑客范儿加科幻感,就像我自己一样!
How the fuck does anyone do anything serious with npm?
谁能正经用npm干点什么事啊?
>>109462411
It's a collaboration problem not a distribution problem.
这是协作问题,不是分发问题。
It's this easy:
就这么简单:
0.0.0.0 registry.npmjs.org
0.0.0.0 registry.npmjs.org(hosts 屏蔽规则:禁用 npm 官方源)
0.0.0.0 npmjs.org
0.0.0.0 npmjs.org(hosts 屏蔽规则)
0.0.0.0 npmjs.com
0.0.0.0 npmjs.com(hosts 屏蔽规则)
0.0.0.0 npmjs.net
0.0.0.0 npmjs.net(hosts 屏蔽规则)
0.0.0.0 npm.im
0.0.0.0 npm.im(hosts 屏蔽规则)
0.0.0.0 yarnpkg.com
0.0.0.0 yarnpkg.com(hosts 屏蔽规则)
>>109459513
the people who "discover" these exploits are often -but not always- the same people who made them in the first place. and the goal is to secure big "security scanning" and "supply chain protection" contracts.
“发现”这些漏洞的人,往往——虽然不是总是——就是当初制造它们的那批人。目标就是为了拿下大额的“安全扫描”和“供应链保护”合同。
showing how relatively easy it is to stop all this destroys the whole business model.
展示这事多容易一刀切掉,直接毁了整个生意模式。
it's funny and ironic how people here can grok the idea of DDoS protection racketeering (a la cloudflare), but not "supply chain" protection racketeering. maybe if we can convince an (((e-celeb))) to float the idea, it will become real in the minds of the retarded.
好笑又讽刺的是,这里的人能懂DDoS保护式敲诈(像Cloudflare那种),却理解不了“供应链”保护式敲诈。也许找个大佬出来吹吹风,傻子们才会当真。
>>109458879
How does this steal secrets? Shouldn't those be stored encrypted? I use SOPS to store my secrets, so even if they get snooped on, shouldn't they be secure? Are people just storing their secrets in plaintext or something?
这怎么偷得到机密?那些不是应该加密存储吗?我用SOPS存机密,就算被偷窥了,也应该安全吧?是不是有人直接把机密明文扔那儿了?
>>109464747
You don't know what secrets are or do, it's so funny.
你根本不懂机密是什么或干嘛用的,太搞笑了。
>>109458879
Why use someone else's package when you can ask Fable to make a non-bloated one doing exactly what you want? People are stupid.
为什么不干脆让Fable写个不臃肿的、正好满足需求的包,非要用人家的?人真是蠢。
>>109465516
Because you can't
因为做不到。
>>109465516
>Fable pulls in the package anyway
>Fable最后还是拉来了那个包
>rugs your api key for 1000b tokens
>骗走你的API密钥去跑1000B tokens
>>109458879
And they want you to just give away your ID info to log in online.
而且他们还想你随便交出身份证信息才能在线登录。
>keyv
A sqlite wrapper for those who are too retarded to even use a piss-easy ORM.
一个给连傻瓜级ORM都用不来的弱智准备的SQLite封装。
Don't worry, only retards and kids were affected.
放心,只有弱智和小孩子中招了。
Also this is the most obvious malware
再说了,这明摆着就是恶意软件。
>>109466231
The issue isn't pulling that package but running a project that is pulling that package
问题不在于拉取那个包,而在于运行一个会拉取那个包的项目。
I use NixOS. How does this affect me?
我用NixOS。这对我有啥影响?
I got roped into working on a pretty substantial JavaScript project. I don't have to make a npm package for it though. Can I just not put it on npm?
我被拉进了一个挺大的JavaScript项目干活。不过我不需要为它做个npm包。我能不能干脆不上传npm?
>>109469588
>I got roped
>我被拉进
what a strange thing to say
这话啥意思
>>109470018
ESL moment
ESL时刻。
at this point, if you update any software, especially those that have additional requirements, and you don't personally verify them safe -- it's your fault.
到了这个地步,你要是更新任何软件,尤其是那些有额外依赖的,而你又不亲自验证它们安全——那就是你自己的锅。
>bah bah i need to update everything and download portable instances of new software that all have 200 line requirements.txts and i don't know how to read code!!!
>咩咩咩我必须更新一切,下载各种便携版新软件,全都带200行requirements.txt,而且我压根不会读代码!!!
suckstart a poptart then, sucker
那就去吸你的Pop-Tart吧,傻逼。
>>109462405
>node.js
node.js is one of the most efficient and powerful runtimes ever made. it literally compiles to machine code in real time, and can ship code with an active run time.
node.js是有史以来最高效最强大的运行时之一。它真的能实时编译成机器码,还能带着活动运行时发代码。
KNEEL.
(如果你觉得这篇文章有启发,可以点击这里付费)