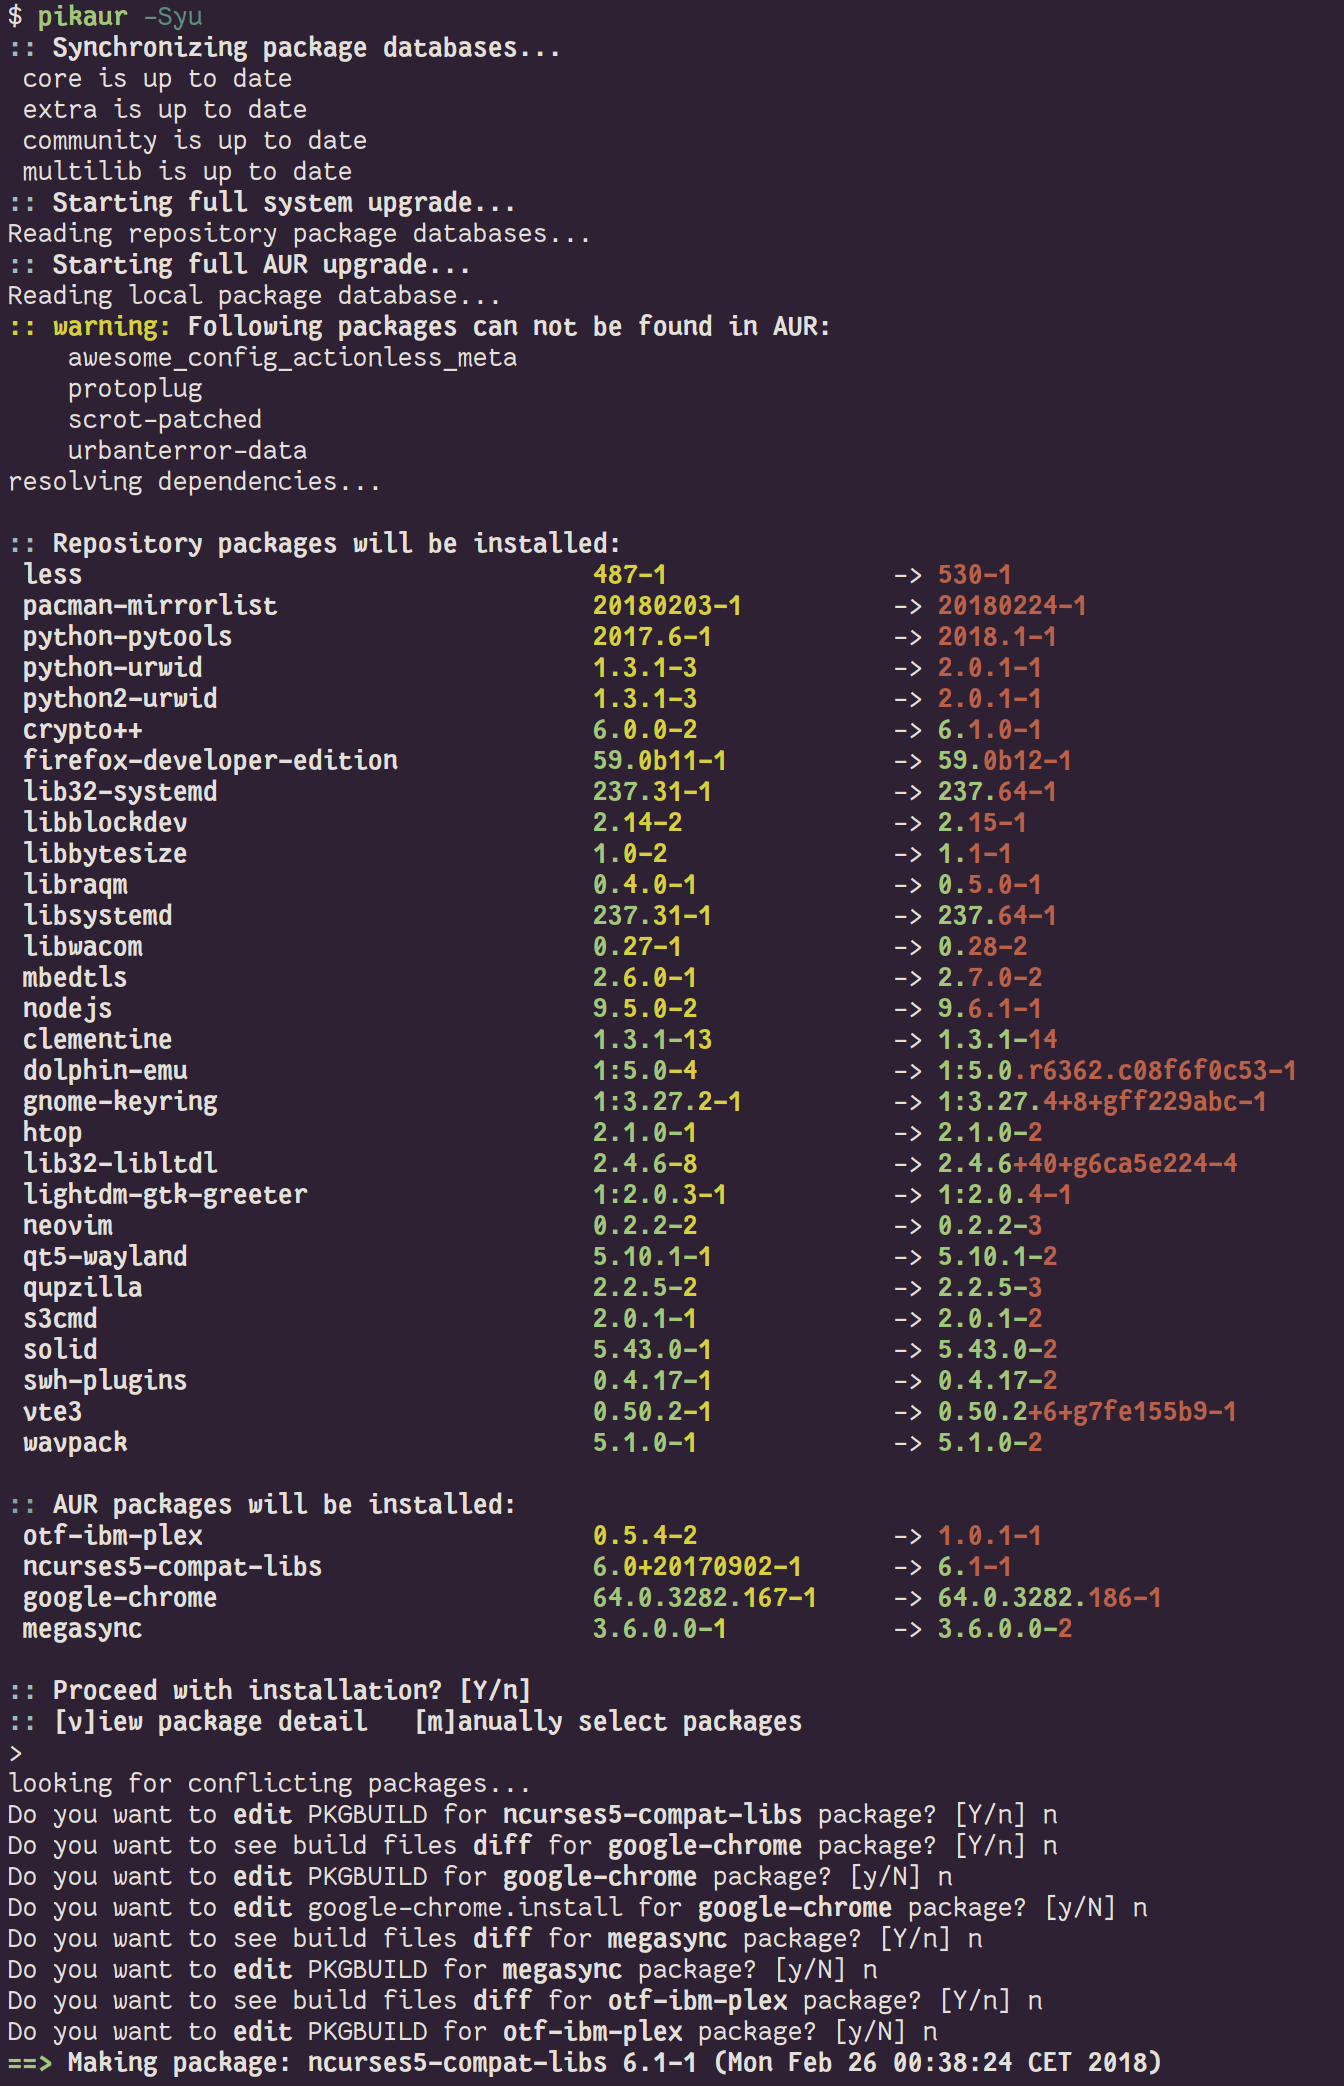
lol lmao
哈哈哈 笑死
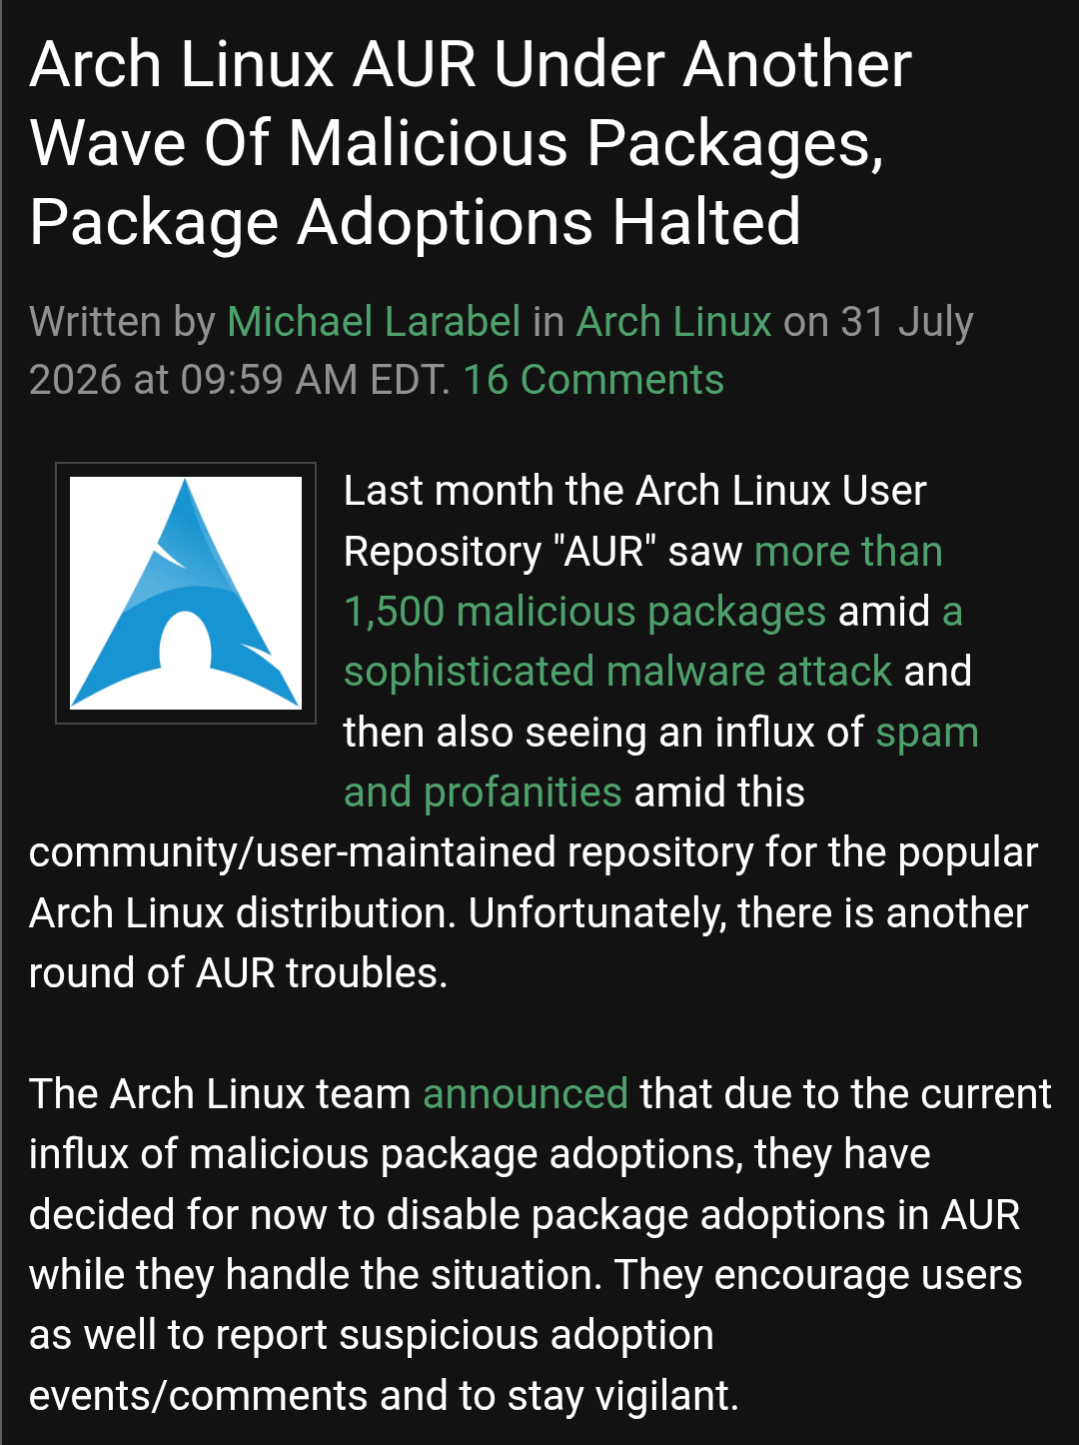
Arch Linux的AUR又遭一波恶意软件包
>>109419858
I use Mint so that's not my problem. My updates move slow like the snailcat. I guess CachyOS anons should just avoid AUR completely because that's the distro that has the most windows refugees now.
我用Mint所以那不关我事。我的更新慢得像蜗牛猫。我觉得CachyOS的anon们应该完全避开AUR,因为那个发行版现在跑进最多的Windows难民。
Linux gaming should have never evolved from frozen bubble and tux racer.
Linux游戏就不该从冰封泡泡和企鹅赛车进化出来。
After the last incident I just switched to using Nix package manager for anything I used to get from the AUR. It's pretty nice.
上次出事之后,我直接改用Nix包管理器来弄以前从AUR拿的东西。挺好用的。
>>109419858
why does linux need to be updooted every day i dont get it
为啥Linux每天都要更新啊我不懂
>>109419858
The inevitable result of every tech YouTuber telling gamers to flock to Linux, specifically Arch-based distros
这是每个科技博主叫玩家们涌向Linux、特别是Arch系发行版的必然结果
>>109419858
just another reason to stay on Bazzite. Honestly this is less of a Linux problem and more of what I have been saying about Arch for a long time:
这就是留在Bazzite的又一个理由。说实话,这与其说是Linux的问题,不如说是我不停吐槽Arch很久的事:
>he needs to stop worrying about land
>他需要别老惦记土地了
>he needs to focus on making pacman more user friendly
>他该集中精力让pacman更好用
flathub doesn't have these problems because it has a vetting process, AUR is ran by the same guy who runs Arch. He is busy getting his dick sucked and playing make believe socialism buying land out in forests and saying socialism works. He has no time to vet the packages on AUR.
flathub没这问题因为它有审核流程,AUR是跟Arch同一个家伙在管。他忙着被口活和扮演社会主义梦,在森林里买地还说社会主义靠谱。他没时间审核AUR的包。
I wondered when this would happen since AUR is essentially the Mod Nexus of arch distros
我早就猜到迟早会这样,因为AUR基本上就是Arch发行版的Mod Nexus
>>109420034
this only affects arch because the developer, yes 1 dude runs the entire show, is buying forests saying
这只会影响Arch,因为开发者——对,就一个人全权操办——在买森林说
>look we have no crime because of socialism!
>看,社会主义下我们没犯罪!
yes he is that fucking retarded.
对,他就是那么脑子有病。
>>109420072
Are you sure you've got that right? There is more than one developer working on Arch. You might mean the project leader, but Polyak isn't the only developer by a long shot.
你确定没搞错?Arch不止一个开发者在干活。你可能说的是项目负责人,但Polyak绝不是唯一开发者,差远了。
>>109420072
I understand you have a political axe to grind, but it really happens because the only thing that kept Linux as safe from viruses as it used to be was the fact that barely anyone used it. The ears of malicious actors perked up during all the buzz about people making the jump to Linux. Arch-based distros like CachyOS got all the attention.
我明白你是有政治立场要掰扯,但这确实会发生,因为以前Linux之所以能像现在这样不容易中毒,纯粹是因为用的人太少。恶意行为者在大家嚷嚷着要转投Linux的时候早就竖起耳朵了。像CachyOS这种基于Arch的发行版出尽了风头。
>>109420072
>>109420103
yeah but he has been told several times that AUR needs a governing process, and as much as I like him IRL, his methods are a bit messy. Socialism doesn't work.
是啊,但他已经被告诉过好几次了,AUR需要一个治理流程,而且就算我在现实中挺喜欢他这个人,他的做法还是有点乱。社会主义行不通。
>>109420118
been saying it for years
我这些年一直在说这话
>the only reason Linux has no viruses is because nobody uses it.
>Linux没病毒的唯一原因就是没人用。
and now people use it, here we are, and Levente refuses to put people in charge over AUR
现在有人用了,结果就这样了,而Levente就是不肯让其他人来管AUR
>that goes against the idea of freedom of expression
>那违背了言论自由的想法
he internally runs AUR and treats it like his personal church
他私下里管着AUR,把它当成自己个人的教堂
I mean no hate towards him, but I and many others have been saying for years that AUR needs a government or this would happen, and here we are.
我不是对他有恶意,但我和其他很多人这些年一直在说AUR需要一个管理机构,不然就会出事,现在果然如此。
>>109420121
boy it's like we have all this proof of what I have been saying for all these years
好家伙,这简直是我们这些年说的所有话的实锤了
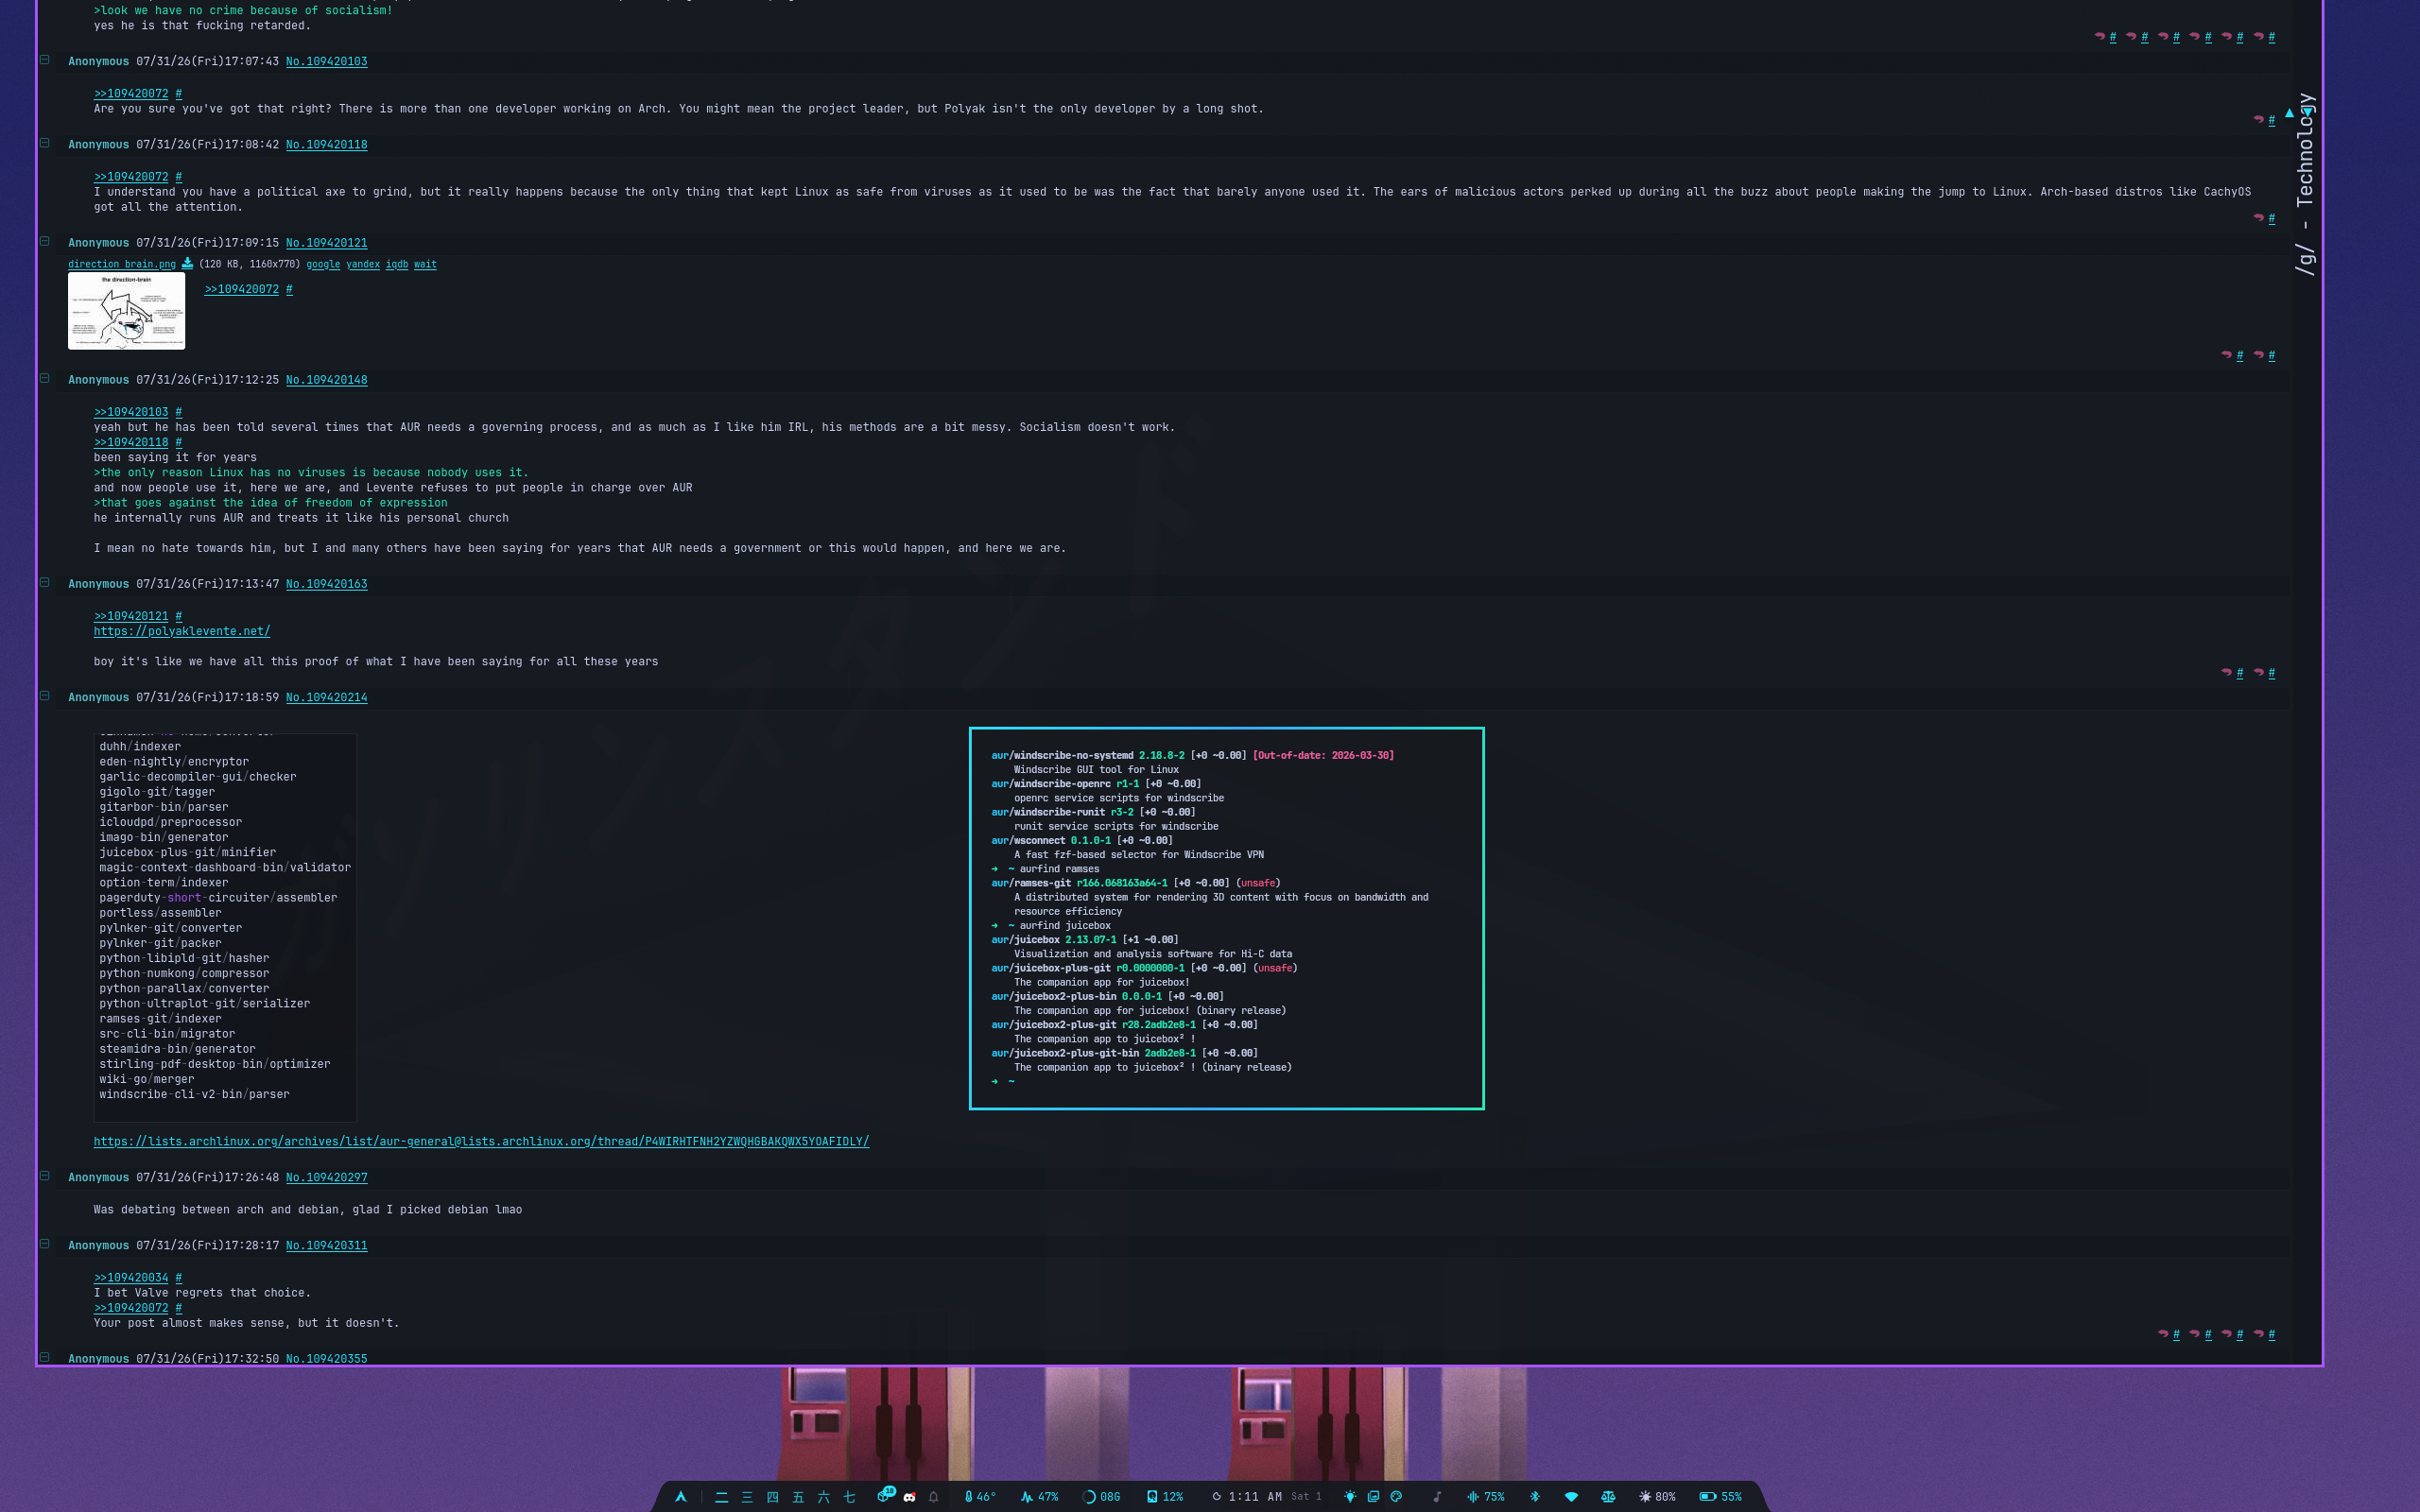
archutil/linter
bigwebapp-manager/minifier
boringssl-git/hasher
cinnamon-no-nemo/converter
duhh/indexer
eden-nightly/encryptor
garlic-decompiler-gui/checker
gigolo-git/tagger
gitarbor-bin/parser
icloudpd/preprocessor
imago-bin/generator
juicebox-plus-git/minifier
magic-context-dashboard-bin/validator
option-term/indexer
pagerduty-short-circuiter/assembler
portless/assembler
pylnker-git/converter
pylnker-git/packer
python-libipld-git/hasher
python-numkong/compressor
python-parallax/converter
python-ultraplot-git/serializer
ramses-git/indexer
src-cli-bin/migrator
steamidra-bin/generator
stirling-pdf-desktop-bin/optimizer
wiki-go/merger
windscribe-cli-v2-bin/parser
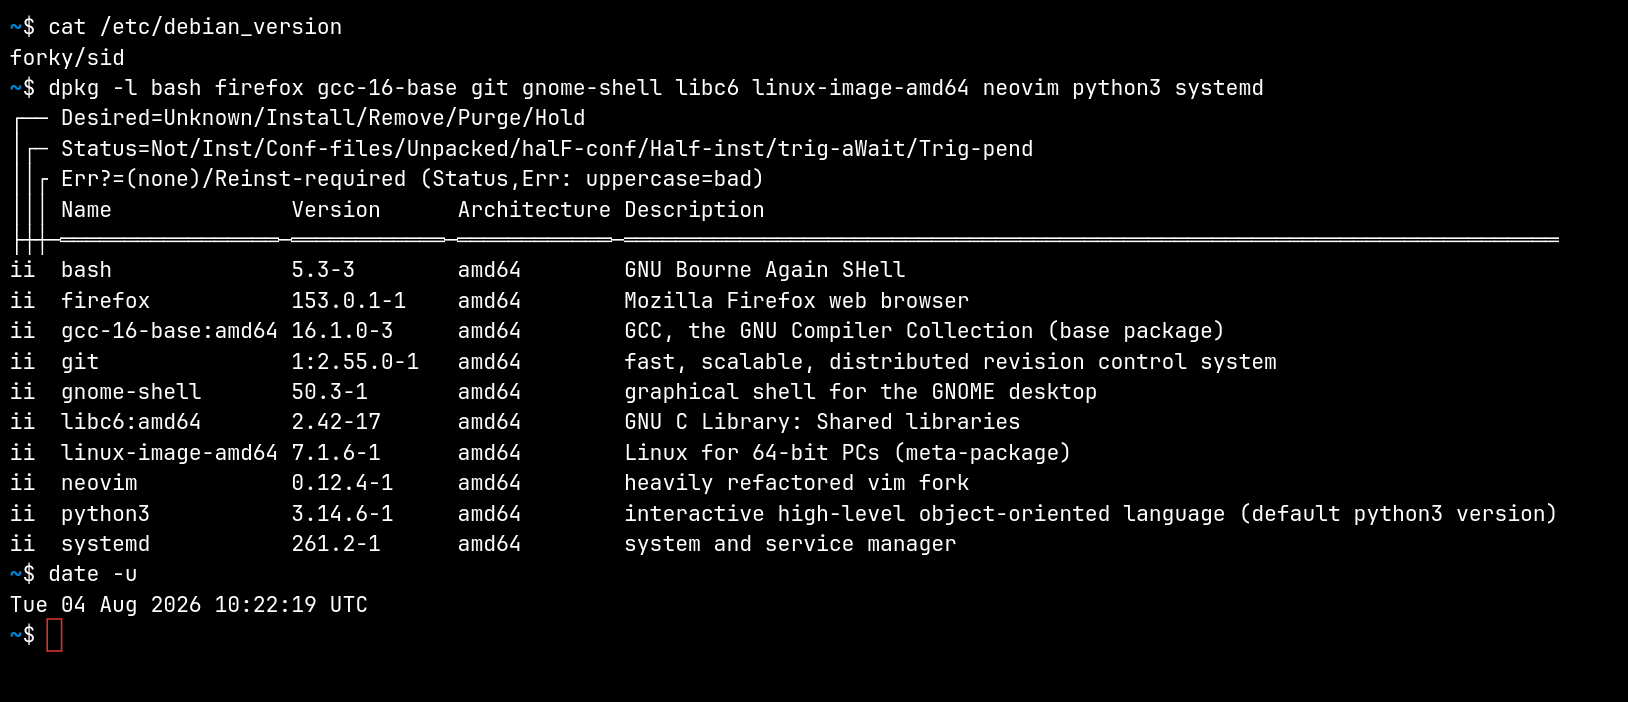
Was debating between arch and debian, glad I picked debian lmao
我之前在arch和debian之间纠结,幸好选了debian,笑死 ≟ 我敢打赌Valve现在后悔那个选择了。
>>109420034
I bet Valve regrets that choice.
我敢打赌Valve一定后悔做了那个选择。
>>109420072
Your post almost makes sense, but it doesn't.
你发的帖子看着有点道理,但实际上没道理。
>>109420311
>I bet Valve regrets that choice.
>我敢打赌Valve现在后悔那个选择了。
Likely not, proper gaming on Linux practically requires rolling release
大概不会吧,在Linux上正经玩游戏基本得靠滚动更新
>>109420311
Not really, AUR is not required to operate Steam OS. Even Arch itself doesn't require AUR. Downloading stuff from AUR has always been optional
真不是,Steam OS运作根本不需要AUR。甚至Arch本身都不依赖AUR。从AUR下东西一直是可选的
Imagine trusting anything but DNF for packages COULDNT BE ME. SAVE ME FROM FUCKING VIRUSES IBM SAMA
想象一下除了DNF还敢信任别的包管理器,反正我不可能。IBM大佬,求你把我们从该死的病毒里救出来吧
>109420355
Don't care, I'm using Fedora KINOite and it just werks.
无所谓,我用的是Fedora KINOite,就是能用。
>>109420163
Sir this is the technology board, /pol/ is that way
先生,这是技术版,/pol/ 在那边
>>109419858
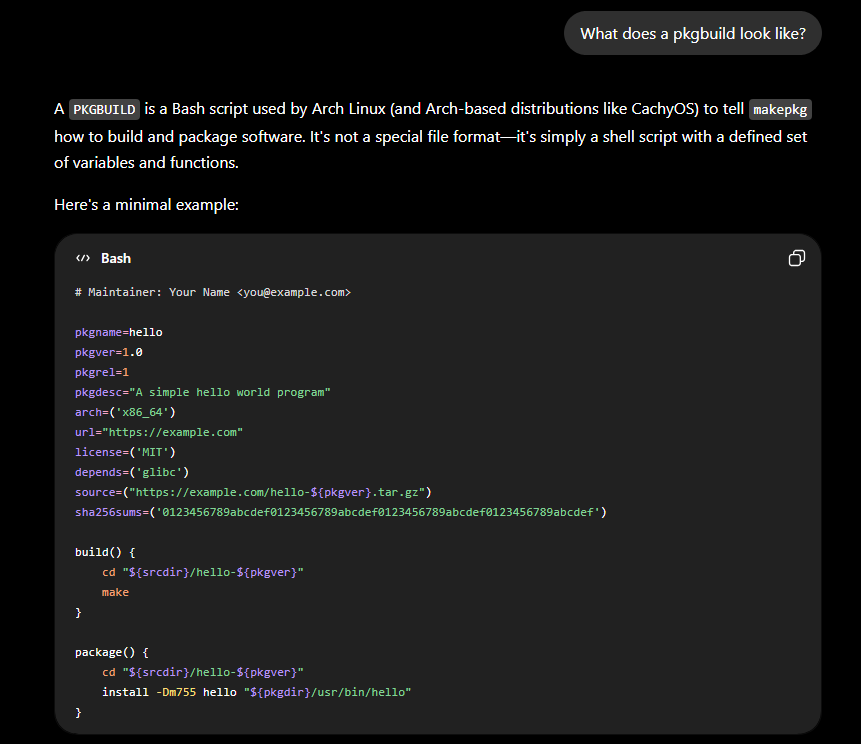
imagine installing anything from AUR automatically and without reading PKGBUILD file.
想象一下有人从AUR装东西连PKGBUILD文件都不看,直接自动装。
>>109420009
Nixpkgs is only slightly less vulnerable. Once the AUR requires email verification or whatever the meme response to the last attack was, it'll reach parity with nixpkgs
Nixpkgs也只是稍微没那么脆弱。一旦AUR要求邮件验证或者随便什么上次攻击后的梗对策,它就会跟nixpkgs半斤八两了
>>109419858
I already thought the way they handled it was bad the first time, it happening again is just embarrassing
我第一次就觉得他们处理得很差,现在又来一遍,真是丢人
>>109419858
Seriously though, how would (You) fix AUR without completely crippling it in the process? Or should they just shut it down?
说真的,要怎么在不彻底搞残AUR的情况下修好它?还是说他们干脆关掉算了?
>>109420941
gate downloading from AUR with a captcha and a quiz for what's inside PKGBUILD.
给从AUR下载加个验证码,再加个关于PKGBUILD里有什么的测验。
>>109420072
>>109420121
>>109420163
>>109420565
/pol/ is not right evendoe yuropeans are not mentally prepared for moslems (malicious submitters) taking a bomb vest or a truck (malicious package) to a pride parade (the aur)
/pol/ 说得没错,虽然欧洲人还没心理准备面对穆斯林(恶意提交者)穿着炸弹背心或者开着卡车(恶意包)去参加骄傲游行(AUR)
>>109420941
Brown zoomers will keep script kidding and attacking this high trust system because they are factually going to get free bitcoins if they keep trying.
棕色系零零后们会继续写脚本胡搞并攻击这个高信任系统,因为他们只要继续试,实际上真的能搞到免费比特币。
They should just wipe the AUR because there's tons of accounts that have invalid emails, so you could theoretically buy a DNS name of an old email service and you have a bunch of old accounts for free to keep fucking it up.
他们就应该整个清空AUR,因为里面有大量账号的邮箱是无效的,所以理论上你可以买一个旧邮件服务的DNS域名,然后就能白拿一堆旧账号继续搞破坏。
Lots of holes in the AUR, aids.
AUR漏洞太多了,害死人。
>>109420991
You could just read the pkgbuild but the 30 year old boomer that has 100 million dollars in bitcoin is not going to read that shit so hackers will keep trying to infosteal him and therefore find more holes in this shit aur system.
你其实可以直接读一下 PKGBUILD,但那个拿着一个亿比特币的老古董是不会去看那玩意的,所以黑客们会继续尝试偷他的信息,从而在这破 AUR 系统里发现更多漏洞。
There's money at the end of the line so the AUR will get solved by 2027
后面有钱赚,所以 AUR 的问题到 2027 年肯定会被解决。
>>109420941
Just put some fucking LLM in front of it to approve if packages are malware or not
就在前面放个什么破 LLM 来审批包是不是恶意软件。
>>109421252
this will make some funny prompt injections.
这肯定会搞出一些搞笑的提示注入。
>>109421277
It would could just flag suspicious packages for human review
也可以只是把可疑的包标记出来,让人工去审查。
>>109421305
I flagged my cock for insertion into phat latina asses.
我把我那玩意儿标记为“插入拉美胖妞屁股”了。
>>109420627
It's always required an email to sign up. That doesn't stop anyone.
注册一直都要邮箱。那也没拦住任何人。
>>109420941
package adoption has been the main issue in the recent attacks.
最近几次攻击里,包接管才是主要问题。
>rate-limit it
>给它们限速
>reputation system for maintainers, limit adoptions based on reputation
>给维护者加个信誉系统,根据信誉限制接管
>require review for people without reputation
>没信誉的人必须走审查流程
>cooldown periods for new releases
>新版本发布要有冷却期
>block 3rd-world countries
>封锁第三世界国家
Same as any other package management really.
其实跟其他任何包管理没啥区别。
>>109419858
no one uses arch for anything remotely serious
没人会用 Arch 干任何稍微正经的事。
>>109419858
>>109420034
>>109420072
>>109420355
This has to be because Steam is easy to grab personal information because workshop has yet to fix the virus problem. Now hackers are targeting Arch because Valve is incompetent at security.
这肯定是因为 Steam 太好偷个人信息了,因为创意工坊还没修好病毒问题。现在黑客盯上 Arch,是因为 Valve 在安全方面太菜了。
>>109421362
Right, but I thought they made a token effort to tighten things up a bit recently
对,但我还以为他们最近好歹做了点样子想收紧一下呢。
>>109421568
This is more that arch is terrible at security.
这更多是因为 Arch 在安全上烂透了。
I always laugh at troonix users that like to go on and on about how a centralized package repo is somehow superior. Just lol, how retarded can you get?
我总是笑那些 troonix 用户,他们老爱吹中央化软件源怎么怎么优越。就呵呵,能蠢成这样也是服了。
>>109421648
aur is still more secure than downloading random exe files. still laughing?
AUR 还是比下载随机 exe 文件安全多了。还笑不?
>>109421682
If you're so stupid and lacking in judgement that you need a group of maintainers to curate your software for you, sure.
如果你蠢到连选软件都需要一堆维护者帮你把关,那随便你吧。
>>109419858
just make your own PKGBUILDS you lazy fucks
自己写 PKGBUILD 啊,你们这些懒鬼。
>>109421648
You know you can also just use winget on windows and download something microsoft allowed right? The difference is AUR isn't monitored at all.
你知道吗,在 Windows 上你也可以用 winget 下载微软允许的东西。区别在于 AUR 根本没人管。
>>109421621
They both are terrible and both should be punished.
两个都烂,两个都该被骂。
>just read the pkgbuild bro
>哥们儿,读读 PKGBUILD 就行了。
by law the malware has to have a virus field that is true or false. jsut make sure the pkgbuild does NOT have this field set to true
按法律规定,恶意软件必须有个“病毒”字段,值是 true 或 false。你只要确保 PKGBUILD 里这个字段不是 true 就行。
>>109420941
>"Arch Linux hacked"
>“Arch Linux 被黑了”
>Someone uploaded malware to an "Arch" branded repo without human gatekeepers that lets anons upload arbitrary scripts.
>有人往一个带“Arch”牌子的、没有人工把关、匿名就能传任意脚本的软件源里传了恶意软件。
Bad PR
>>109421682
not really, I'd argue SmartScreen screeching the moment you try to run anything that isn't signed is still gonna stop more retards than downloading shit from the AUR
还真不一定,我觉得 SmartScreen 在你跑任何没签名的东西时立刻狂叫,还是能拦住更多傻逼的,比从 AUR 下载破玩意强。
though there's an argument to be made that people who download random AUR shit without reading the PKGBUILDs are the same that would just click "run anways" on Windows so who knows
不过也可以说,那些不看 PKGBUILD 就从 AUR 乱下东西的人,跟 Windows 上直接点“仍然运行”的是同一批人,谁知道呢。
>>109420004
This. You're going to have to switch to Plan9 if you want to avoid the normies now.
没错。要想躲开这群小白,你得改用 Plan9 了。
>>109420941
Mandatory ID verification.
强制实名验证。
>>109422083
>by law
>按法律规定
That's RFC 3514, and the IETF does not make laws, yet.
那是 RFC 3514,而且 IETF 目前还不立法。
>>109420941
>fix AUR
>修复 AUR
It appears to be working as intended, the problem is the users.
看起来这是按预期工作的,问题出在用户身上。
>>109422679
>RFC 3514
LMAO I forgot about that one.
笑死,我都忘了那个了。
And now they've unironically published RFC 8890
然后他们居然一本正经地发布了 RFC 8890
Repositories suck.
软件仓库烂透了。
>>109419985
>using mint
>用 mint
>instead of just a normal version of debian without the faggotry
>而不是装个正常的 debian 版本,不带那些傻屌玩意儿
you are retarded and a faggot.
你就是个傻逼,还是个基佬。
>>109420311
>grug says thing
>grug 说了句话
>grug no understand how steam os works
>grug 不懂 steam os 是怎么工作的
classic /g/
/g/版经典发言
>>109423216
only arch. they've been warned for a very long time about how vulnerable their ecosystem is to an attack by just random schizos.
只有 arch。他们早就被警告过很多次了,他们的生态对一群随机疯子的攻击有多脆弱。
>>109423247
>>instead of just a normal version of debian without the faggotry
>>而不是装个正常的 debian 版本,不带那些傻屌玩意儿
I'm sorry i'm not an expert in being a faggot like you. If i wanted to install debian i would just instal LMDE just for you to seethe anyway but i decided to install Ubuntu without the faggotry=Mint.
抱歉,我不是你那种专家级别的基佬。如果我想装 debian,我直接装 LMDE 就完了,纯粹为了看你抓狂,但我最后决定装个不带傻屌玩意儿的 Ubuntu = Mint。
>>109419858
installed arch on yet another machine today
今天又在另一台机器上装了 arch
what do i even need the AUR for? just ignore it lmao
我到底还需要 AUR 干嘛?直接忽略它不就完了,哈哈
>>109423372
Ubuntu is faggotry set to maximum flaming mode. you dodged a bullet.
Ubuntu 就是把傻屌玩意儿开到最大火力的模式。你躲过了一颗子弹。
>>109419858
>sophisticated malware attack
>复杂的恶意软件攻击
It was literally adopting AURs that were abandoned and pushing malware ffs.
实际上就是接手了被遗弃的 AUR 包然后塞恶意软件,就这么回事。
There is nothing sophisticated about this.
这压根没什么复杂的。
>>109420041
flathub does not have a vetting process.
flathub 没有审核流程。
But every single distro repository does.
但每个发行版的软件仓库都有。
>>109419858
The AUR was a mistake.
AUR 就是个错误。
I saw the writing on the wall after the xz utils supply attack. Moved off of rolling release since.
在xz utils供应链攻击后我就看到了苗头。从那以后就离开了滚动发布。
>>109423822
Pretty funny that you would reference xz here when:
你在这里引用xz还挺好笑的,因为:
>To our knowledge the malicious code which was distributed via the release tarball never made it into the Arch Linux provided binaries, as the build script was configured to only inject the bad code in Debian/Fedora based package build environments.
>据我们所知,通过发布压缩包分发的恶意代码从未进入Arch Linux提供的二进制文件中,因为构建脚本被配置为只在基于Debian/Fedora的软件包构建环境中注入坏代码。
went to nixos after arch. then tried use debian with nix installed. nixpkgs has turned out to be a great AUR replacement for my needs. using hyprland-git on debian trixie. only thing i cant use is the hyprland screen locker because debian patches its polkit to use a different syscall from every other linux distribution uses for some reason. so i used swaylock. if i ever go back to arch. it will not be using the AUR but with nixpkgs.
我是从Arch转到NixOS的。然后试着在装了Nix的Debian上用。对我来说,nixpkgs已经成了AUR的绝佳替代品。我在Debian trixie上用hyprland-git。唯一用不了的是hyprland的屏幕锁,因为Debian给它的polkit打了补丁,用的系统调用跟其他所有Linux发行版都不一样,鬼知道为啥。所以我用了swaylock。要是哪天我回Arch,也不会用AUR,而是用nixpkgs。
>>109424122
whaddap my nixxer
咋样啊,我的Nix兄弟
let's post pictures of our buttwholes as is customary
按惯例,咱们来发屁眼照片吧
>>109424122
That's comparing apples to oranges, nixpkgs is the official Nix repo, the AUR is an unmoderated user repository
这比较不对等啊,nixpkgs是官方的Nix仓库,AUR是没人管的用户仓库
>>109424146
you first
你先来
>>109424147
and its great. and you can use it on any linux distro. the system level shit needs some workarounds if you absolutely need it. but if i needed the nix system level shit, id just install nixos.
而且它很好用,你可以在任何Linux发行版上用。系统级的东西如果你非要的话需要一些变通。但如果我需要Nix的系统级功能,我干脆直接装NixOS。
>>109419858
all arch problems can be fixed by only using pacman
所有Arch问题都能靠只用pacman解决
>>109419858
whats the point of using the AUR?
用AUR有啥意义?
can those tards not just bulid from source?
那些傻逼就不能直接从源码编译吗?
>>109421568
>This has to be because Steam is easy to grab personal information because workshop has yet to fix the virus problem.
>这肯定是因为Steam容易拿个人信息,因为创意工坊还没修复病毒问题。
Wait what? Is the workshop compromised?
等等啥?创意工坊被攻破了?
Makes me glad I haven't used Steam in years.
让我庆幸好几年没用Steam了。
>>109421568
with the pace that valve updates steamos nothing will make it through
以Valve更新SteamOS的速度,啥都过不来
also a great reason to use the flatpak version of steam
这也是用Steam Flatpak版的好理由
>>109424232
If you're willing to build from source then surely auditing a pkgbuild is no big deal.
如果你愿意从源码编译,那审计一个PKGBUILD肯定不是啥大事。
>>109424325
even for people who know how to build from source, using a package manager is just more convenient. its just unfortunate that the AUR had basically no moderation or even a vetting process. luckily that the ABS is not the only source based package manager.
就算知道怎么从源码编译的人,用包管理器也更方便。只是可惜AUR基本没监管,连个审核流程都没有。幸好ABS不是唯一基于源码的包管理器。
>>109419858
I can't take this clownery anymore.
我再也受不了这种傻逼闹剧了。
I think I will switch to gentoo.
我想我会转去Gentoo。
>>109419858
good thing I only have gzdoom installed
幸好我只装了gzdoom
>>109423247
>>instead of just a normal version of debian without the faggotry
>>而不是装个正常的 debian 版本,不带那些傻屌玩意儿
that's just mint, you retarded nigger faggot
那纯粹就是Mint,你这个傻逼死基佬
>>109420311
Valve doesn't use AUR in any capacity, retard. If valve wants a package in arch repos it's happening.
Valve压根不用AUR,白痴。要是Valve想让包进Arch仓库,那早就进了。
>>109424259
Workshop is not compromised, games have vulnerabilities and some allow running arbitrary code. It's possible to distribute this code using workshop mods if the game supports workshop and allows mods to run arbitrary code with full system access.
创意工坊没被攻破,游戏有漏洞,有些允许运行任意代码。要是游戏支持创意工坊并允许mod以完全系统权限运行任意代码,那就能通过创意工坊mod传播这种代码。
>>109425128
>adds faggotry
>加了基佬元素
>thinks that's debian sans faggotry
>觉得那是不带基佬元素的Debian
you sir, are the homosexual ficus.
您啊,就是棵同性恋榕树。
>>109420034
they're not though. all of the tech youtubers telling people to switch to linux for gaming are telling them to use bazzite. that's fedora based.
他们才不是呢。所有那些吹Linux打游戏的科技博主都在叫人用Bazzite,那是基于Fedora的。
>>109424386
literally the best linux distro on the planet, unironically. you won't regret your choice.
说实话,这真的是地球上最好的Linux发行版,一点不夸张。你不会后悔这个选择的。
>>109420214
good to see my AUR helper wrapper that tracks the malicious packages and annotates them on searches with yay, pacaur, or paru is picking up the new wave of malicious packages like it's supposed to.
很高兴看到我的 AUR 助手包装器能正常工作,它能追踪恶意软件包,并在用 yay、pacaur 或 paru 搜索时标注它们,正好赶上了新一波恶意软件包。
>>109425302
How does it determine what's unsafe? Is there an API somewhere or it just has a hardcoded list that has to be constantly updated?
它是怎么判断什么是不安全的?是有某个 API 还是只是硬编码列表,得不断更新?
>>109423578
It's good to see they put all that on one page. I already knew all of that but it's good to have a resource to refer to.
很高兴他们把那些都放在一个页面上。我早就知道了,但有个资源可以引用还是不错的。
The fact that Flathub has not had a single compromised application published speaks for itself.
Flathub 从来没有发布过哪怕一个被攻破的应用程序,这件事本身就说明问题了。
>>109425307
hardcoded list that is constantly updated, with a cronjob that runs a LLM and has it search every 6 hours for reports of new malicious packages, then it updates the lists. users can type 'aur_safety update' to grab the most recent version of the lists (i encourage them to do it at least once a day) from the git repo so they don't have to pull and re-install the package all over again
硬编码列表,持续更新,有个 cronjob 跑着一个 LLM,每 6 小时搜索一次新恶意软件包的报告,然后更新列表。用户输入 'aur_safety update' 就能从 git 仓库拉最新版列表(我建议他们至少每天拉一次),不用重新下载安装整个包。
>>109423977
That's not as good as it sounds when you realise that the compromised code WOULD have made it there if the attacker didn't actively disable it in certain circumstances.
等你意识到如果攻击者没有在某些情况下主动禁用代码,那些被攻破的代码本来就会上线,这就没那么好听了。
>>109419858
Arch Linux is not a serious distro. Most Archbabbies are probably running around with an exceedingly barebones installation and zero thought of hardening or security because doing anything like this on Arch requires you to be a Linux admin (or thereabouts) and treating your install like a full time job. Installing Arch through the installation instructions leaves you with the single most basic Linux install you can possibly have, and yet these posers think it makes them some kind of h4x0r for doing so.
Arch Linux 不是个正经发行版。大多数 Arch 宝宝大概都跑着极其精简的安装,根本没想过加固或安全,因为在 Arch 上做这些事要求你是个 Linux 管理员(或差不多水平),还得把安装当全职工作来对待。按安装说明装完 Arch,得到的就是最基础的 Linux 安装,但这些装逼犯还觉得这样自己就成了什么黑客高手。
>inb4 "da aur isn't technically part of arch"
>先说了,"aur 严格来说不是 arch 的一部分"
Yeah, it's not, and if you were to not count it, Arch's package repositories would be miniscule. That's why people use it. Because it is required for so much shit in Arch, because the base package repos are so tiny. The Aur is a malware repository masquerading as a package repo, Anne Frank-ly it's amazing it took this long to be abused like this.
没错,不是,如果你不算它,Arch 的软件仓库就小得可怜。这就是为什么人用它。因为 Arch 里太多东西全靠它,因为基础包仓库太小了。AUR 就是个伪装成软件仓库的恶意软件库,坦率说,能被这么滥用已经是拖了很久的事了。
>>109419858
societal trust is eroding and you're laughing
社会信任正在崩塌,你还在笑
>>109421601
You obviously thought wrong
你显然想错了
>>109420041
>and saying socialism works
>还说社会主义行得通
does he have downs syndrome?
他是不是有唐氏综合征?
>>109425318
>hardcoded list that is constantly updated
>硬编码列表,持续更新
where is this? I downloaded a few packages but I need to know for sure
这个在哪?我下载了几个包,但我需要确认一下
>>109419858
I love Mint.
我爱 Mint。
>>109419858
>Arch Linux AUR Under Another Wave Of Malicious Packages
>Arch Linux AUR 再遭恶意软件包攻击
fake news faggot
假新闻,傻逼
>>109419858
Who is attacking the AUR with malware and why?
谁在用恶意软件攻击 AUR,为什么?
>>109419858
>user repository
>用户仓库
>surprised there is malware
>居然惊讶有恶意软件
are you retarded?
你他妈是智障吗?
you do not have to use the aur and if you do you are supposed to check the pkgbuilds.
你不需要用 AUR,如果用了,你就该检查 pkgbuild。
>>109425557
using arch is basically being a sysadmin for your pc
用 Arch 基本就是给自己电脑当系统管理员
when i started using arch other arch users told me that stuff like apparmor or a firewall were not necessary lol
我开始用 Arch 时,其他 Arch 用户告诉我 apparmor 或防火墙之类的东西没必要 lol
I don't give a shit, I am using Arch for 8 years or so and never needed the AUR.
我根本不在乎,我用 Arch 大概 8 年了,从来不需要 AUR。
CasshewsOS users don't have to worry because they have a repository that replaces the AUR for most needs
CasshewsOS用户不用担心,因为他们有一个仓库,能在大多数需求下替代AUR。
>>109420941
Doesn't OBS work properly?
OBS不是正常工作吗?
>>109426482
>when i started using arch other arch users told me that stuff like apparmor or a firewall were not necessary lol
>当我开始用Arch时,其他Arch用户告诉我像AppArmor或防火墙这种东西根本没必要,呵呵
Yeah see, so many of them are dumb. They think they're hot shot but their installs are the most basic, rickety thing ever. Arch can't even install with secure boot turned on, and most of its users probably don't even know what secure boot does.
是吧,看吧,他们里好多都是笨蛋。他们觉得自己很牛,但他们的安装是最基础、最摇摇欲坠的破玩意。Arch连开着安全启动都装不了,而且大部分用户可能根本不知道安全启动是干嘛的。
>arch is for experienced users, you should not what you do, for an example knowing what you install
>Arch是给有经验的用户用的,你应该知道自己在干嘛,比如清楚自己装了什么
>hurr durr i use arch btw
>嘿嘿嘿我用的Arch顺便说一句
Typical.
>>109421012
are there other methods the aur can be compromised besides pkgbuilds?
除了PKGBUILD之外,AUR还有别的被入侵的方式吗?
>>109420034
Linux users will have to install an antivirus just like in windows. Oh, the irony
Linux用户也得像Windows一样装杀毒软件了。哦,真是讽刺
>>109426500
CachyOS is truly the best. I don't know why more people don't use it.
CachyOS真的是最好的。我不明白为什么没更多人用它。
>>109426710
Because "it reeks of gaymer, ick"
因为“它一股游戏宅味,恶心”
>>109426710
This but unironically. It's measurably faster than other distros (sans Gentoo if you coompile the same way CachyOS does) and it just werks.
这话我是认真的,不是反讽。它确实比其他发行版快,能实测出来(除非你用和CachyOS一样的方式编译Gentoo),而且就是好用。
>>109426710
Cachytranny is the new manjaro
Cachytranny就是新的Manjaro
>>109419858
anyone has some AUR package that can scan if i installed infected malware aur user package?
有没有人能推荐个AUR包,能扫描我是不是装了感染了恶意软件的AUR用户包?
or some terminal cli command?
或者有没有终端命令行?
>>109425274
>>thinks that's debian sans faggotry
>>觉得那就是去掉娘炮味的Debian
it is factual that debian comes with all the faggotry and mint has to avoid it like its a carcinogen
事实就是Debian自带一堆娘炮玩意,而Mint得像躲致癌物一样躲开它
go check if your debshit has pushed for more DEI internships to cover up for their pedophile leaders, retarded slave.
去查查你的垃圾Debian是不是又推了一堆DEI实习生来掩盖他们恋童癖领导的事吧,蠢奴隶。
>>109426482
you 100% already have iptables/nftables already installed when you installed arch. the default settings are fine
你装Arch的时候100%已经带iptables/nftables了。默认设置就挺好的。
>>109426552
you can easily enable secure boot on arch, sbctl is in the repo all you have to do is put secure boot into setup mode and follow the wiki it details how to use sbctl, after that anytime you run mkinitcpio it'll check if you're signed
你很容易就能在Arch上开启安全启动,sbctl就在仓库里,你只需要把安全启动设成设置模式,然后跟着Wiki走,它详细讲了怎么用sbctl,之后每次跑mkinitcpio它都会检查你是否签名了。
>>109420012
It doesn't.
它没有。
>>109426941
>you 100% already have iptables/nftables already installed when you installed arch. the default settings are fine
>你装Arch的时候100%已经带iptables/nftables了。默认设置就挺好的。
are they?
真的吗?
>>109420118
>the only thing that kept Linux as safe from viruses as it used to be was the fact that barely anyone used it
>让Linux以前那么安全不受病毒侵扰的唯一原因就是几乎没人用它
No, it's because it's inherently more secure than Microsoft operating systems. You think servers aren't also targets of viruses?
不,是因为它本质上比微软的系统更安全。你觉得服务器就不是病毒的目标了?
>>109420941
They should shut it down. The AUR was always a fundamentally terrible idea.
他们应该把它关掉。AUR从来就是个根本性烂主意。
>>109425268
>It’s not hacked
>它没被黑
>It’s hacked
>它被黑了
Steam is no longer safe anon, their “Trust me bro” nonsense lead to the arrest of criminals by the FBI. All because Steam lied about safety. Now you here defending Valve for lying.
Steam也不安全了,匿名者,他们那套“信我兄弟”的屁话导致FBI抓了罪犯。全是因为Steam在安全问题上撒谎。现在你在这儿替Valve撒谎辩护。
>>109420956
They could do a [Y/N] prompt for every directive in it.
他们可以对里面的每条指令都弹个[是/否]提示。
>>109421844
For one-off stuff just download the source and put it in /opt/ yourself. No need to bother with the package manager.
一次性用的东西,直接下载源码放到/opt/里自己搞定就行。没必要去麻烦包管理器。
>>109425319
It also only worked with Systemd and an increasingly large number of "arch" users are really on Artix.
而且它只支持Systemd,而现在越来越多的“Arch”用户其实用的是Artix。
>>109427143
M$ has like 50% of the server maket also.
微软在服务器市场也占了大概50%的份额。
>>109427442
>>109427143
>>109420118
It's because normally the only way you install packages is you build them from the source or you wait for repo maintainers to look at new releases, build them, package them and distribute them.
因为通常你安装软件包的唯一方式就是从源码编译,或者等着仓库维护者查看新版本、构建、打包并分发它们。
AUR leapfrogs that for the sake of convenience with the same consequences you have one Windows. IMO it's good to have the option but you have to understand the risks and how to mitigate them. "Just don't" is good general advice.
AUR为了便利跳过了这一过程,后果和你用Windows时一样。我觉得有选项是好事,但你必须明白风险以及如何规避。“干脆别用”是个不错的通用建议。
>>109427437
the package manager is just for easier updating. i can mass check and update any packages i want
包管理器只是为了方便更新而已。我可以批量检查和更新任何我想更新的包。
>>109427462
How often are you updating obscure unpackaged software that git pull && make && sudo make install is too inconvenient?
你多久会更新一次那种小众的、未打包的软件,以至于git pull && make && sudo make install都嫌麻烦?
>>109427472
>i'll completely add words to your post that you didnt say and quesiton you based on my own addtion
>我会完全在你没说过的话上添油加醋,然后根据我自己加的内容来质问你
Man fuck Arch, I'm going to install NixOS
妈的,去他的Arch,我要装NixOS。
>>109427501
I can't believe president Nixon has his own linux distro.
我简直不敢相信尼克松总统也有自己的Linux发行版。
i looked at the affected packages and you have to be a retard to install those
我看了受影响的那些包,装那些玩意儿的人得是多傻逼。
>>109427621
are you going to keep using arch after this shitshow?
这一出闹剧之后你还打算继续用Arch吗?
>>109427629
yes?
>oh no, le hecking openssl1.1-bin got hijacked!!!
>哦不,天杀的openssl1.1-bin被劫持了!!!
why were you installing this in the first place?
你当初为什么要装这玩意?
>>109427621
It's still a big step to go from completely safe to something a retard could hurt themselves with.
从完全安全到傻逼都能伤到自己,这仍然是个大步跨越。
It was always a theoretical issue but to have it realized is a big deal.
这之前一直是个理论问题,但真的发生了就是大事。
genuinely comical seeing arch trannies telling us that the AUR isn't important and that they never pushed it as the reason to switch to arch
看着Arch粉跟我们说AUR不重要、他们从来没拿它当转Arch的理由,真是好笑。
>>109427682
its not about that
不是这个原因
of course im never going to install random aur packages
我当然永远不会装那些随便来的AUR包
but it looks really bad for arch, constantly be on the news about malware "attacks"
但这对Arch来说很难看,老是因为恶意软件“攻击”上新闻
the arch maintainers need to take it seriously, not whatever the fuck they did after last months wave
Arch的维护者必须认真对待这事,而不是上个月那波之后干的那堆破事
>>109424122
this is how good you could have it if you weren't so surveillancephobic /g/
如果你没那么怕监控,你能过得多好啊 /g/
>>109419858
>spam and profanities
>垃圾帖子和脏话
Not profanities! *clutches balls*
脏话!*捂住蛋蛋* ┘ 你电脑根本不上网,为什么要apparmor和防火墙?
>>109426482
Why do you need apparmor and firewall when your computer isn't even connected to the Internet?
你的电脑都没联网,为什么还需要 AppArmor 和防火墙?
>>109419858
i use botnet btw
我用的是僵尸网络,顺便说一下
>>109419858
The malware only started after cachyOS
恶意软件是在CachyOS之后才开始出现的
>>109427442
Got a source for that? I don't believe you.
有来源吗?我不信你。
>>109420214
>All literally trash packages
>全是垃圾包
>>109428705
>Arch loses it's reddit moderator
Arch 失去了它的 Reddit 版主
Oh, the horror! I'm sure they'll manage without him.
哦,太可怕了!我肯定他们没他也能行。
>>109422279
Is BSD next on the chopblock?
BSD会是被下一个“砍掉”的对象吗?
>>109419858
this is what happens when you treat a gentoo-style hacker distro as a production one
这就是当你把Gentoo那种黑客风格的发行版当作生产环境来用时会发生的事。
the standard (pre-2021) advice has always been to treat the aur as a starting point for your own pkgbuilds that you personally manage, akin to how user overlays are supposed to be forked for your own needs
标准的(2021年前的)建议一直是把AUR当作你自己管理PKGBUILD的起点,就像用户overlay应该被fork以满足你自己的需求一样。
most people using arch (and especially its derivatives) are better served on fedora
大多数用arch(尤其是它的衍生版)的人,其实用fedora更合适。
Is Fedora the only sane alternative to Arch? Debian is too slow.
Fedora是不是唯一比Arch更理性的选择?Debian太慢了。
>>109419858
how hard is it to simply not let anyone take over orphaned packages without telling any potential downloaders that it changed ownership
不让任何人在不告知潜在下载者所有权变更的情况下接管孤儿软件包,这到底有多难?
freeze that specific package forever, whoever takes it over gets a renamed version
永远冻结那个特定包,谁接管它就换个名字重新发布
if someone wants it as a dependency they'll test it before requiring it
如果有人想把它当依赖,他们会在要求之前先测试它
>>109419858
>be me, take up hobby
>是我,开始搞个爱好
>the internet: [this hobby] has been infiltrated by XYZ and is detrimental to YOU EXPLICITLY
>互联网:[这个爱好] 已经被XYZ渗透了,对你明确有害
>me: *leave hobby*
>我:*放弃爱好*
>me: *take up new unrelated hobby*
>我:*开始搞个不相关的新爱好*
>the internet: [this hobby] has been infiltrated by XYZ and is detrimental to YOU EXPLICITLY
>互联网:[这个爱好] 已经被XYZ渗透了,对你明确有害
>be me: *leave hobby*
>是我:*放弃爱好*
>be me: *take up new, completely unrelated hobby, which i invented myself*
>是我:*开始搞个全新的、完全不相关、我自己发明的爱好*
>somehow, the internet: [THAT NEW HOBBY WHICH ONLY YOU KNOW ABOUT] IS DETRIMENTAL TO YOU EXPLICITLY, STOP IT BECAUSE XYZ
>不知怎么的,互联网:[那个只有你知道的新爱好] 对你明确有害,因为XYZ快停掉
yeah, i dont care, i'm going to continue using arch linux, unless i find a new OS that fits my taste.
是啊,我不在乎,我会继续用arch linux,除非我找到个更合口味的新系统。
>here's why the way you're doing [your hobby] is wrong
>这就是为什么你搞[你的爱好]的方式是错的
>you NEVER knew about these things about [your hobby]
>你从来不知道关于[你的爱好]的这些事
its the same clickbait meta that youtube content creators used these last 15+ years.
这就是youtube创作者过去15多年用的同款标题党套路。
this is why i hate all forms of click based content.
所以我讨厌所有点击类内容。
>>109426391
she's cute, but i prefer henya.
她挺可爱的,但我更喜欢henya。
>>109429501
>whoever takes it over gets a renamed version
>谁接管它就换个名字重新发布
that's formally known as a "fork"
那正式叫“fork”
>>109419858
looks like im staying on atomic fedora
看来我要留在atomic fedora上了
>>109419858
arch being called a meme for a reason
arch被说成梗是有原因的
>>109419858
I am convinced Fedora and Fedora derived distros are doing this because Fedora and it's derivatives are losing popularity to Arch based distros like CachyOS.
我确信Fedora和Fedora衍生发行版这么做,是因为Fedora和它的衍生版正在输给CachyOS这类基于Arch的发行版。
>>109419858
desu I pretty much never use anything on AUR any more anyway I used to years ago, but if your only option is the AUR normally there a better alternative.
说真的我现在几乎不再用AUR上的任何东西了,以前用过几年,但如果你的唯一选择是AUR,通常有更好的替代方案。
Fuck this.
操他妈的。
Is there any tool to check if I have the malware or not?
有没有工具能检查我是否中了这个恶意软件?
How did it even get back?
它到底怎么回来的?
Should I update now or is it still compromised?
我该现在更新还是它仍然被入侵着?
>>109425557
why are all arch haters so misinformed and retarded?
为什么所有arch黑子都这么无知又傻逼?
>>109427331
You are retarded. Nobody hacked workshop. The mods were valid and uploaded through normal means, they even contained no suspicious files. The game just gave mods the ability to run arbitrary power shell commands.
你脑子有病吧。没人黑掉创意工坊。那些mod都是正常上传的合法mod,里面甚至没有可疑文件。只是游戏本身让mod能运行任意PowerShell命令。
The only practical solution valve has is to delete workshop. Or alternatively make workshop support exclusive to a very small number of trusted and vetted games. Clearly this game shouldn't be allowed to be modded.
Valve唯一实际的解决办法是删掉创意工坊。或者让创意工坊只支持一小部分可信赖且经过审查的游戏。显然这游戏不该允许被mod。
>>109429358
yeah i was going to learn to to write my own PKGBUILDs
对,我当时打算学着自己写PKGBUILD。
but if it gets to that point, isnt it better to use a distro with bigger repositories, or where third party software makes official packages for your distro (deb, rpm)
但要是到那地步,用个仓库更大、或者第三方软件会为你的发行版做官方包(deb、rpm)的发行版不是更好吗?
>>109432203
Someone did idiot: https://escorenews.com/en/csgo/news/53826-valve-fixed-critical-exploit-that-allowed-to-access-cs2-inventory-via-workshop-maps
Valve clearly lied about fixing workshop maps and mods. Stop believing in their lies.
Valve明显在修创意工坊地图和mod这事上撒谎了。别再信他们的鬼话。
>>109426842
>getting your info from Jewduck
>从Jewduck那儿获取信息
Give me one reason to care about your opinion.
给我一个在乎你观点的理由。
>>109432502
Cs2 is a completely different game turbo retard. This is like saying Microsoft fixing a bug in windows didn't fix it in Linux.
CS2是个完全不同的游戏,你tm智障吧。这就跟说微软修了Windows的bug却没修Linux的一样。
>>109430404
Red Hat doesn't care because, much like Canonical with Ubuntu, they already dominate the spaces that matter to them (enterprise). They would give less of a shit about the end user, which is why Fedora is stuck as RHEL's beta testing grounds.
Red Hat不在乎,因为跟Canonical之于Ubuntu一样,他们已经在他们关心的领域(企业级)占主导了。他们对最终用户根本不上心,这也是为什么Fedora一直困在当RHEL的测试场。
>>109419858
>Why are people panicking about this?
>为啥大家这么恐慌?
>This is fucking retarded.
>这傻逼透了。
Like, check the fucking PKGBUILD, dumbass.
就说,你tm去看下PKGBUILD啊,蠢货。
But if you by accident forget to read it, and you may have installed malware,
但如果你不小心忘了看,可能已经装了恶意软件,
>run the command: echo "Affected Packages Found:"; comm -12 <(pacman -Qq | sort) <(curl -s https://cscs.pastes.sh/raw/aurvulnlist20260611.txt | sort) | { read -r l && printf '%s\n' "$l" || echo "None. No known compromised packages are installed."; } to make sure you didn't install malware.
>>109432515
That happened too: https://linuxsecurity.com/news/vendors-products/windows-update-fixes-linux-dual-boot-boot-issues
You’re stupid
你就是蠢。
>>109432855
Oh god, you're too retarded to be real. This isn't even analogous, who the fuck was talking about dual booting? Fuck off dude, it's exhausting to talk to someone as dim as you.
老天,你蠢到不像真的。这根本不类比,谁tm在说双系统了?滚吧,跟你这种智障说话实在太累。
>>109420012
Because C is shit and AIs are finding new bugs everyday.
因为C语言垃圾,AI每天都在发现新漏洞。
>>109425240
>Valve
Yeah, very cute misdirection, you stupid fuck.
对,很可爱的转移话题,你这个傻逼。
>>109419858
AUR malware checking tool, will determine if you have been fucked.
AUR恶意软件检测工具,能判断你有没有被人搞了。
>>109432542
I'm not fucking curling anything
我tm才不会去curl任何东西。
>>109420072
>is buying forests saying
>买森林是这么说
>look we have no crime because of socialism!
>看,社会主义下我们没犯罪!
Are you schizo or do you have a rational reason for stringing together two unrelated things?
你是精神分裂还是有啥合理理由把两件无关的事扯一块?
>>109419858
The dipshit Arch devs/community think that this is some survival of the fittest thing, and celebrate when anyone runs malware through software they host and encourage people to use. I don't think I've ever seen an archfag happier than when they can chastise/put down anyone asking for help with this sort of thing
这帮傻逼 Arch 开发者/社区觉得自己搞的是什么适者生存,谁要是通过他们托管并推荐的软件跑了恶意程序,他们反而乐开花。我从来没见过比这更开心的 arch 傻逼,一边训斥一边贬低任何为这种事求助的人。
>Did you see the warning on the arch wiki?
>你看到 Arch wiki 上的警告了吗?
>Did you READ the pkgbuild? Huh? Did you read it? You DESERVE it you little bitch
>你读 PKGBUILD 了吗?嗯?读了吗?你活该,小婊子。
etc. I clearly remember the losers in #archlinux on irc banning people just respectfully asking if anything was going to be done to block AUR while the last attack in June was ongoing. A nasty, toxic community where the members feel glee at talking down to others (when the vast majority of these people are just retards that copy/paste shit from a wiki and rice desktops).
等等。我清楚记得,六月份上次攻击进行时,IRC 上的 #archlinux 频道里那些 loser 直接封了那些只是礼貌地问“有没有计划封堵 AUR”的人。这真是个恶心又充满敌意的社区,成员们以居高临下跟人说话为乐(而这些人绝大多数不过是照抄 wiki、折腾桌面的蠢货)。
I wish Arch in its current form dies and is replaced by a Valve led fork of it.
我希望 Arch 现在这种形态赶紧死掉,被 Valve 主导的 fork 取代。
>>109434097
AUR does not host software. It hosts pkgbuilds.
AUR 不托管软件。它托管的是 PKGBUILD。
>>109419858
it’s only going to get worse when ai bots are hammering it 24/7 until the end of time with malware
等 AI 机器人 24/7 不停往里面灌恶意软件直到天荒地老,情况只会更糟。
>>109434110
Oh look mimsy, another retard! The AUR is a git repo you chucklefuck, and therefore it can and does host binaries. The latest attack includes packages that add a malware binary which is called from the PKGBUILD.
哟,看啊 mimsy,又来一个傻逼!AUR 是个 git 仓库,你他妈搞清楚点,所以它完全可以也确实托管二进制文件。最近的攻击里就有包带了恶意二进制,然后从 PKGBUILD 里调用。
Why am I not surprised that an arch defender doesn't know what they're talking about?
为什么我对 Arch 的辩护者根本不懂自己在说什么一点都不惊讶?
>>109425318
Can you post the repo? The arch devs / community seem to think posting an official known list is like pulling fingernails or something so they absolutely expect you to dig around in the mailing list or reddit or wherever the fuck
你能贴下仓库吗?Arch 开发者/社区好像觉得公开一份已知名单比拔指甲还难,所以他们就指望你去邮件列表或者 reddit 或者什么鬼地方自己翻。
>>109432542
>Man who can't read chastises others for not being able to pick out tiny details in a crappy script file
>一个自己读不懂的人,还骂别人看不出一坨劣质脚本里的小细节
Many such cases! Try reading these words: This is a new attack, so your vuln list from the last one is not useful.
这种例子多了去了!试着读读这句话:这是一次新攻击,所以上次那个漏洞列表没用。
>>109419858
>use meme, tranny coded distro
>用 meme 发行版,还是镶了变性人代码的那种
>get hacked
>被黑了
>>109419858
I hope all the gaymer manchildren on cachyos got hacked in the ass
我希望 cachyos 上所有 gaymer 大少爷都被爆菊式黑客攻击。
>>109420163
>/pol/ack le vent
>/pol/ack 风起
>>109429391
Debian testing, but it's technically a development branch and doesn't get dedicated security support
Debian testing,但严格来说它是开发分支,没有专门的安全支持。
>>109431768
Explain which parts of that post are wrong
解释下那帖子哪里错了。
>>109419858
My gentoo system doesn't have this problem.
我的 gentoo 系统没这问题。
>>109423247
what would you remove from debian to remove "the faggotry"?
你要从 Debian 里删掉什么才能去掉“那堆娘炮玩意儿”?
There's nothing in it.
里面啥都没有。
Unless you mean SunnyDlight but then you'd just run Devuan.
除非你指的是 SunnyDlight,但那样你直接跑 Devuan 不就得了。
>>109434688
everyone knows that gentoo users are compiling 24/7 instead of actually using their computers so there is no point in such attacks
谁都知道 gentoo 用户一天到晚在编译,根本没在真正用电脑,所以攻击他们没意义。
>>109419858
Why are Dindus attacking Arch ? is it really about the normies ?
为啥 Dindus 在攻击 Arch?真就为了那些普通人?
>>109435234
It takes like 5 minutes for anything that isn't a Chromium or based on Chromium like qtwebegnine
只要不是 Chromium 或基于 Chromium 的东西(比如 qtwebengine),也就五分钟的事。
>>109419858
Tye concept of arch linux is retarded in the first place. Who needs to be forced to update everything every few days? Even Microsoft pushes out updates once a month.
Arch Linux 这概念本身就蠢。谁需要被迫每隔几天就更新所有东西?连微软都一个月才推一次更新。
Fuck this shit.
去他妈的吧。
Just finished transitioning my AUR packages over to a staged local package repository built with makepkg and repo-add, and removed paru and yay. Now I can update and audit them at my own cadence.
刚把我的一批 AUR 包迁移到了用 makepkg 和 repo-add 搭建的本地分段仓库,还卸载了 paru 和 yay。现在可以按自己的节奏更新和审查它们了。
Vibe coded some scripts to automate the process.
随手写了一些脚本来自动化这个过程。
>>109435259
You mean webkit?
你是指 webkit 吗?
>>109423247
You have filtered yourself as a moron. Debian is one of the most inclusive open source projects. Hahahahaha you fucking retard you should join the Debian Women's mailing list, I heard they allow troons like you.
你把自己过滤成了个白痴。Debian 是最包容的开源项目之一。哈哈哈哈哈你个傻逼,你应该去加入 Debian 女性邮件列表,我听说他们允许你这种货色加入。
>>109419858
Been thinking of jumping distros. Anyone use PikaOS?
一直在考虑换个发行版。有人用过 PikaOS 吗?
>>109431543
Halp?
>>109427103
i want the person who took this photo to die. Immediately.
我希望拍这张照片的人去死。立刻。
>>109432932
Getting offended because you ask if Microsoft did something wrong to Linux by updating their operating system and anon delivered is why your whiny behavior isn’t acceptable in /g/ return to /v/ cultist Sheep.
你因为问微软更新系统有没有对 Linux 做什么坏事而生气,然后有人回答了你,这就是为什么你这副哭唧唧的样子在 /g/ 不受待见,滚回 /v/ 去吧,邪教信徒羊。
>>109419858
Anyone else got malware from these?
有人从这些东西里中过恶意软件吗?
Being blamed for letting a PKGBUILD slip something nefarious through is like blaming someone for not spotting every possible mole on their body that could be cancerous. Imagine you get diagnosed with skin cancer and the derm/oncologist tells you "Hey fuck you, you didn't catch this one mole so you deserve this"
因为让 PKGBUILD 漏了可疑内容就被怪罪,就像怪一个人没发现身上每一颗可能癌变的痣一样。想象你被诊断出皮肤癌,皮肤科/肿瘤科医生跟你说“嘿去你妈的,你没抓到这颗痣,所以你活该”。
>>109426552
>Arch can't even install with secure boot turned on
>Arch 连开了安全启动都装不上
this is wrong, the installation image that they distribute is not signed, but you can sign it with your own certificate to make it boot
这是不对的,他们分发的安装镜像没签名,但你可以用自己的证书签名让它启动。
>most of its users probably don't even know what secure boot does
>大多数用户可能都不知道安全启动是干嘛的
at least secure boot is covered in detail in the arch wiki
至少 Arch wiki 里安全启动讲得很详细。
sudo pacman -Syu
在论坛语境下,这句命令本身就是原样保留的(它是 Linux 命令,不是普通文本),无需翻译。如果您需要我翻译它的含义,那就是:“使用 sudo 权限执行 pacman 的系统更新命令(-Syu,即同步、升级所有软件包)”。但按您的要求,输出应为: sudo pacman -Syu
not my problem
不关我的事
I'm really considering moving to NixOS or using system-manager with Arch as base.
我真在认真考虑转到 NixOS,或者用 system-manager 以 Arch 为基础。
>>109419858
If linux distributions and package managers won't adapt some sort of LLM based antivirus-filechecker, entire linux is kill.
如果 Linux 发行版和包管理器不搞点基于 LLM 的杀毒文件检查器,整个 Linux 就完了。
>>109438893
>>109419858
AUR, more like OUCH
AUR,不如叫 OUCH。
>install random unverified software from the internet
>从网上装随机未验证的软件
>get hacked
>被黑了
wtf how could arch do this to me??
卧槽 Arch 怎么能这么对我??
>>109437407
Yeah PKGBUILDs have to be proof-engineered. Making sure that they are safe is something that you need a doctorate or college degree in order to do because of how complicated they are.
是啊,PKGBUILD 必须得像工程证明一样来搞。确保它们安全这事得有博士学位或大学学历才能做到,因为它们太复杂了。
>>109435542
yay will tell you if a package has been orphaned or adopted.
yay 会告诉你一个包是被遗弃还是被接管了。
>>109419858
Glad II moved to Fedora. At least for now.
还好我换到Fedora了。至少暂时安全。
>>109419985
Wasn't their default repository completely separate from AUR?
他们的默认仓库不是跟AUR完全分开的吗?
>>109444344
nigger...
I'm on cachyos but I used the AUR to install things like chrome because it wasn't in pacman
我在用CachyOS,但我用AUR装chrome这类东西,因为pacman里没有
am I retarded
我是不是傻逼
You wanted more people to adopt Linux? You got your wish granted
你不是希望更多人用Linux吗?心愿实现了
>>109444358
>>109444364
was a reply to you before you deleted the post
这是回你的,在你删帖之前
>>109444651
can you answer my question
你能回答我的问题吗
I'm safe right?
我没事对吧?
How do I even check to make sure I'm not getting pwned when I download shit?
我下载东西时怎么才能查清楚自己有没有被黑?
>>109444364
I mean my gut instinct is to say yes, you are retarded. If you aren't verifying the pkgbuilds then yes for sure.
我直觉就说,没错,你就是傻逼。你要是不验证PKGBUILD,那肯定就是了。
>>109444877 (me)
I also want to say that Arch being marketed as a starting distro by retarded influencers like pewdiepie are a lot of the reason this AUR shit is a big deal. People like >>109444680 don't understand what they're getting into. Arch is an enthusiast's distro and you really should be a programmer or something similar if you want to use it.
我还想说,Arch被PewDiePie那帮傻逼网红当入门发行版推广,很大程度就是这AUR破事闹大的原因。像>>109444680这种人不明白自己到底在碰什么。Arch是给发烧友用的发行版,真要拿它当日常用,你起码得是程序员或类似的人。
To answer your question, here is the list of affected packages >>109420214
回答你的问题,受影响软件包清单在这 >>109420214
>>109444877
How do you verify them?
这玩意儿怎么验证?
How are you supposed to install things that aren't in pacman if the AUR isn't safe?
要是AUR不安全,那不在pacman里的东西该怎么装?
i never trusted the AUR and had like 5 packages installed from it
我从来没信过AUR,就装过5个包
i always checked the PKGBUILD and checked the diffs on every update
我每次都检查PKGBUILD,每次更新还看diff
how hard would be to start writing my own PKBUILDs for the few packages i might need that are not on the arch repos?
自己写PKGBUILD来搞定那几个不在Arch仓库里但可能需要的东西,这有多难?
>>109431543
If you don't know, assume you have malware, format and reinstall, then don't use AUR. Or install an actual distro instead.
不懂的话就当自己中了恶意软件,格式化重装,然后别碰AUR,或者干脆装个正经发行版。
>>109434560
Just run Sid.
直接滚Sid不就完了。
>>109439524
Because Arch has become a popular choice with newbs and gamers for some reason, when it's really a neckbeard hobbyist OS and they should be using Bazzite or even Mint instead. The AUR has also been shilled hard as a selling point where you can get any package you want, glossing over the fact it's a pile of unvetted shit.
因为Arch不知为啥成了萌新和游戏玩家的热门选择,可它明明是给胡子大叔折腾用的系统,他们该去用Bazzite或者干脆Mint。AUR还被吹成万能卖点,说什么想要啥包都行,却避而不谈那上边全是没审核过的一堆垃圾。
On a long enough timeline I think this is going to happen to every distro eventually, unless you are running Gentoo and have the time to review every single diff.
时间线拉长点看,我觉得这事儿迟早轮到每个发行版头上,除非你跑Gentoo,有时间去审每一行diff。
I'm wondering how best I can protect myself for when it eventually happens to mine.
我也在琢磨,等哪天轮到我自己头上,怎么才能防得最稳。
Reduce package count to the absolute minimum required for QEMU, and then run everything else in a VM?
把包数量砍到QEMU最低需求,剩下全扔虚拟机里跑? ⟦ 不,这不会成为所有发行版的未来,因为别的仓库真有测试和审核流程。Arch这些年一直在把责任和活儿甩给用户,这发行版还引以为傲地搞个安装脚本,只支持x86,连带桌面环境的镜像都不出。大多数发行版是照着Arch的路子学,但不是反过来。它就是个小众系统,终于因为懒得搭正经基础设施而遭报应了。你要是真在乎最稳的防护,去整openBSD或QubeOS。
>>109445804
No, this is not going to be the future of all distros because other repositories have actual testing and review. Arch has been offloading responsibility and labor to their users for years, the distro proud itself on having a setup script, it only supports x86, and don't even release images with a desktop environment. Most distros do what Arch do, but not the other way around. It's a niche distro that finally is getting what it deserves for not giving a damn to setup proper infrastructure. If you do care about the best protection, get openBSD or QubeOS.
不,这不会成为所有发行版的未来,因为其他仓库有实际的测试和审查。Arch多年来一直把责任和劳动推给用户,这个发行版以拥有安装脚本为傲,只支持x86,甚至连带桌面环境的镜像都不发布。大多数发行版是照着Arch的方式做,但不是反过来。它是个小众发行版,现在终于因为不在乎搭建正经基础设施而得到应有的回报。如果你真在意最好的保护,用openBSD或QubeOS。
>>109445838
Who is reviewing? Do you know them personally?
谁在审?你跟他们认识吗?
I'm not comfortable betting my life savings, and my business, on people that I don't know, working for free, to do their job perfectly for an infinite amount of time.
我可不敢把毕生积蓄和生意押在一群素不相识、免费干活、还得指望他们永远不出错的人身上。
It won't happen the same way as this attack, but it could still happen via bribery, blackmail, social engineering, negligence of the reviewers, attacker getting lucky, who knows.
不会跟这次攻击同个套路,但还能靠贿赂、敲诈、社工、审核员疏忽、攻击者走狗屎运啥的来搞,谁知道呢。
>>109445897
By that logic then don't go outside at all because something may happen to you.
按这逻辑,那就干脆别出门了,反正说不定会出事。
>>109445920
Do you often carry your life savings around with you outside?
你出门经常随身揣着毕生积蓄?
going to ubuntu. tired of this shit
转Ubuntu了,这破事受够了。
how do I know if an aur package is malicious or not?
我咋知道一个AUR包是不是恶意的?
>>109436216
why? lmao
为啥?哈哈笑死。
it was me btw
其实是我干的,说一声。
>>109445897
>It won't happen the same way as this attack
>不会跟这次攻击同个套路
It won't happen at all. It could theoretically happen, but it won't
根本不会发生。理论上有可能,实际不会。
How to avoid this problem:
怎么避开这问题:
Add the following to your bashrc/zshrc
往你的bashrc/zshrc里加下面这段:
#before every update, run
#每次更新前,跑一下
archinfo(){
yay -Pww
耶——Pww
yay -Ps
耶 -Ps
}
#read the news and notice what packages that yay -Ps reports as orphaned. Either remove those packages or add the to the ignore list in pacman.conf, like:
#看公告,留意yay -Ps报出来是孤儿包的都有哪些。要么卸掉,要么加到pacman.conf的忽略列表里,比如:
#IgnorePkg = <orphaned package> <orphaned package>
#IgnorePkg = <孤儿包名> <孤儿包名>
#then, update
#然后,更新
archupdate(){
#sudo reflector ...
好的,我准备好了翻译内容,请发送需要翻译的英文论坛帖子。
yay -Syyu
耶 -Syyu
#some other package manager, like cargo or cpanm
#其他包管理器也一样,像cargo或cpanm
}
>>109420941
Limiting typo squatting and orphaned packages should generally do the trick.
限制好拼写仿冒和孤儿包,基本就能防住了。
>>109447314
i use paru just because it makes -Pww completely unnecessary. i don't know why yay doesn't implement NewsOnUpgrade. you can also set FileManager to something like lf and if you keep old PKGBUILDs, you can compare diffs.
我用 paru 就是因为用不着 -Pww 了。不懂为啥 yay 不搞 NewsOnUpgrade。你还可以把 FileManager 设成 lf 之类的,要是留着旧的 PKGBUILD,就能对比 diff。
>>109448884
>>109448884
yay shows me the diff for every package I update and the pkgbuild for every package I install. I don't use a terminal file manager because I'm not a larper.
yay 会给我显示每个要更新包的 diff,还有每个要装包的 pkgbuild。我不用终端文件管理器,因为我不是装逼的。
>>109448907
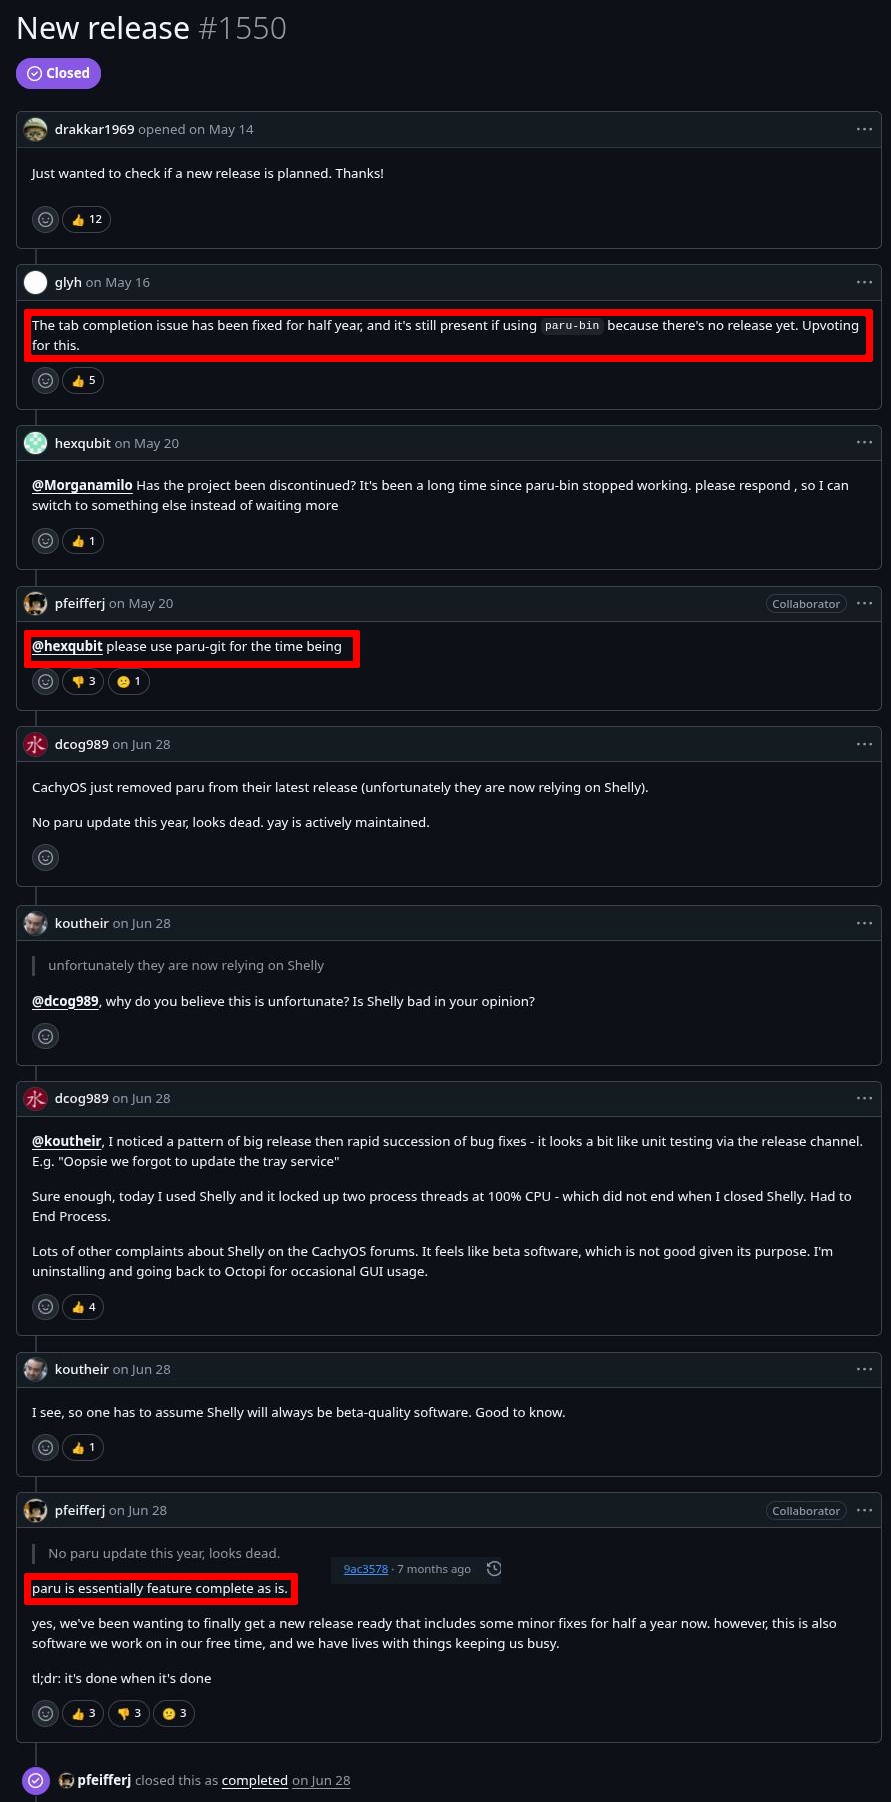
>feature complete
>功能完整
so it'll work forever with no breaking changes?
所以这玩意儿永远能跑,不会有破坏性更新?
>>109448925
i don't normally use one either, i only use it to look at paru's diffs since it's fast and the preview pane is useful. i'm already in the terminal when i update, i might as well stay in it.
我平时也不用这玩意儿,只是拿它看 paru 的 diff,因为快,预览窗也好用。反正更新的时候人已经在终端里了,干脆不挪窝。
>>109448948
If it "worked forever," then they wouldn't need to do 6 months worth of bug fixes. You don't say "use paru-git even though that's the thing you're saying isn't working correctly. It's feature complete. We'll fix it."
要是真"永远能跑",他们犯不着花六个月修 bug。你不能一边说"用 paru-git",一边又说它跑得不正常。"功能完整,我们会修的"这话不对劲吧。
>>109448884
>i don't know why yay doesn't implement NewsOnUpgrade
>不懂为啥 yay 不搞 NewsOnUpgrade
yay -Pww
耶——Pww
yay -Syyu
耶 -Syyu
wow! So hard to figure out. That should totally be a setting.
哇!这都猜不出来。这玩意儿就该做成设置项。
>>109444286
CachyOS? I mean just like Arch you can use AUR if you want. Some retarded gaymers were doing it all the time before this shit happened
CachyOS?我的意思是跟 Arch 一样,你想用 AUR 就用呗。出事之前那些傻逼游戏佬一直都在这么干。
>>109419858
>just read the pkgbuild
>读一下 pkgbuild 不就得了
what's the problem, exactly?
到底有啥问题?
>>109449737
op can’t read
楼主不识字呗
>>109445771
Yeah because CachyOS is genuinely a great Distro, that's why people use it
那当然,CachyOS 确实是好发行版,所以才有人用。
Bazzite is good as well but some may not like an immutable Distro.
Bazzite 也不错,不过有些人可能不喜欢不可变发行版。
>>109450122
I've never used Cachy but if they're taking Arch and turning it from a tinkertranny hobbyist distro into something useable then fair enough. But that's not what I'm referring to. The meme of noobs using Arch as some mainstream gaming distro predates Cachy.
我没用过 Cachy,但如果他们能把 Arch 从折腾佬专属发行版变成能日常用的东西,那没毛病。但我说的不是这个。菜鸟拿 Arch 当主流游戏发行版这个梗,比 Cachy 早多了。
>>109434097
Yeah, there is lots of reddit tier toxic positivity in Arch, but its generally true that you need to know your shit and have some common sense before you install Arch and download stuff from AUR. The Arch install wizard, and CachyOS-SteamOS have been more of a net negative than good for Arch itself though.
没错,Arch 社区里一堆红迪那种有毒的乐观主义,但大体上,装 Arch 之前你得懂点门道、有点常识,再从 AUR 下东西,这话没错。Arch 安装向导还有 CachyOS-SteamOS 对 Arch 本身来说,净影响是负面的。
That being said, a major problem is that Arch users and contributors have been regurgitating these "read the pkgbuild" sayings for so long, they have either forgotten how to harden their OS with the simple, logic-based solutions, they are just that lazy and blame the end user as a comfortable deflection, or maybe this commie philosophy of Arch doesnt work as good as it is supposed to be.
不过话说回来,大问题是 Arch 用户和贡献者把"读 pkgbuild"这句话念叨太久了,要么忘了怎么用简单的逻辑方案加固系统,要么就是懒,甩锅给终端用户当挡箭牌,再要么就是 Arch 这套共产哲学压根没想象中好用。
It took the previous AUR infestation for the AUR maintainers to finally stop allowing ppl with burner mails to adopt orphaned packages. Like why the fuck they allowed that in the age of bots and vibecoders? That shit alone says alot about the people who run Arch and AUR.
上次 AUR 被祸害了一轮,维护者才终于不让用一次性邮箱的人接管孤儿包。为啥当初在机器人满天飞、vibecoder 横行的时代还允许这事儿?光这一点就够说明 Arch 和 AUR 那帮人是什么德性了。
God only knows what other retarded ideas they apply or what elephants in the room they dont adress as they run this Arch-AUR shit show
鬼知道他们还有啥弱智想法,或者在这个 Arch-AUR 烂摊子上还有啥明摆着的问题不去管。
if i want to install shit from the AUR that isn't in any other package manager, but the AUR isn't safe, what am I supposed to do?
那我要装个 AUR 里才有、其他包管理器都没有的东西,可 AUR 又不安全,我该咋办?
are flatpaks better?
flatpak 更好使?
Just get Nobara
直接上 Nobara 吧
>>109451850
Learn how to compile and build packages yourself. The Aur is just a helper, let it help you build them yourself. Dont rely on Aur helper software or the Aur, learn to use makepkg instead and build packages inside an archlinux docker container or something similar.
自己学会怎么编译和构建包吧。AUR只是个辅助工具,让它帮你把包构建出来。别依赖AUR的辅助软件或AUR本身,学会用makepkg,在archlinux的docker容器或类似环境里自己构建包。
>>109447082
there are two aur package scanners, one llm backed and one not
有两个AUR包扫描工具,一个基于LLM,一个不是。
pick one or both and write a little wrapper for yay or whatever you use
选一个或者两个都用,然后给yay或者你用的工具写个小包装脚本。
>>109451982
What is actually involved in doing that?
具体要做些什么?
>>109452153
What are they called?
它们叫啥名?
>>109452269
aur-scanner
aurscan-manticore-release-git
aurscan-manticore-release-git(一个 AUR 软件包名)
>>109452153
is yay or paru better?
yay和paru哪个更好?
>>109452382
paru is unmaintained
paru已经没人维护了。
>>109452269
>What is actually involved in doing that?
>具体要做些什么?
see the arch wiki, start with "makepkg".
去看Arch Wiki,从“makepkg”开始。
PKGBUILD files contain everything you need from the aur.
PKGBUILD文件里包含了从AUR获取所需的一切。
Im vetting the PKGBUILD text files with upstream devs manually, checksums and versioning.
我在手动和上游开发者一起审查PKGBUILD文本文件,核对校验和和版本号。
Its as simple as `makepkg -sic` in the same directory as the PKGBUILD text file.
简单来说就是在PKGBUILD文件所在目录里跑`makepkg -sic`就行。
So say you want google-chrome, download the pkgbuild into a directory, say google-chrome, cd into that directory and run `makepkg -sic` after you have vetted the PKGBUILD text file and the contents it wants to download to your machine, like are the urls correct, do that checksums match and if they dont edit the PKGBUILD to match the upstream checksums and urls etc.
比如你想要google-chrome,把pkgbuild下载到一个目录,比如google-chrome,cd进那个目录,先审查好PKGBUILD文本文件以及它要下载到你机器上的内容,比如URL对不对、校验和是否匹配,不匹配就编辑PKGBUILD改成上游的校验和和URL等等,然后跑`makepkg -sic`。
Years ago we all built programs from svn's etc, makepkg just makes it easier, even easier when you use an AUR helper program.
以前我们都从svn之类的地方构建程序,makepkg只是让这更简单了,用AUR辅助程序更是省事。
But the risks involved now are getting ridiculous, so its time to revert to the old ways and maybe just install gentoo.
但现在风险越来越离谱了,是时候退回老办法,或者干脆装个Gentoo得了。
>>109453075
* To add, you should know what the pkgbuild wants to do to.
*补充一下,你也得知道pkgbuild到底想干什么。
Like what are the build() and package() commands doing, do they look right?
比如build()和package()这些命令在干嘛,看起来对不对?
This is why normies have no idea when it comes to building packages from source and think its just like installing an .exe
这就是为什么普通人根本不懂从源码构建包,还以为跟装个.exe一样简单。
>>109420941
You can't fix it.
没得救。
AUR is user submitted packages and that's just antithetical to security and maintainability. For user packages, they have to be created by the site's system administrator in house. Only packages maintained by the distribution can be shared with other site installations.
AUR是用户提交的包,这本来就和安全可维护性背道而驰。用户包应该由站点系统管理员内部创建。只有发行版维护的包才能分享给其他站点安装。
Shut it down, and people should move to a proper professional distribution like Red Hate Enterprise Linux with a proper support contract.
把它关了吧,大家应该转到正规的专业发行版,比如“红帽恨企业Linux”,再签个正规的支持合同。
>yet another psyop from The Powers That Be to get the AUR taken away from us
>又是“幕后势力”搞的心理战,想把AUR从我们手里夺走。
I use paru for the AUR
我用paru来搞AUR。
Should I switch to yay? is it better?
我该换yay吗?它更好吗?
>>109454033
yes. paru is unmaintained. read the repos from time to time.
该换。paru已经没人维护了。时不时去看看仓库就知道了。
>>109453261
>people should move to a proper professional distribution like Red Hate Enterprise Linux with a proper support contract.
>大家应该转到正规的专业发行版,比如“红帽恨企业Linux”,签个正规的支持合同。
Imagine paying $180 for a redhat licence when i can download and install almalinux or rockylinux.
想想花180美元买红帽授权,而我直接下个AlmaLinux或RockyLinux装上都行。
I wont get the same level of customer support but im not a retard either.
客户支持档次是不一样,但我也不傻。
>>109454310
is there anything wrong with it that needs to be fixed?
它有什么大问题需要修吗?
I chose it over yay because it uses the same syntax as pacman, and apparently it runs faster
我选它而不是yay,因为它跟pacman语法一致,而且好像跑得更快。
the pacman build for paru is somewhat recent
paru 的 pacman 构建版本算是比较新的了
Why is google chrome not in the official repository?
为什么 google chrome 不在官方源里?
Should I switch to the flatpak?
我应该换成 flatpak 版本吗?
>>109419858
>aur
nobody cares.
没人在乎。
it's summer, there's always some scriptkiddie group getting into some shenanigans. has happened without fail every summer for over a decade.
现在是夏天,总会有群脚本小子搞些幺蛾子。十多年来年年夏天必出事,一次不落。
>>109420012
>why does linux need to be updooted every day i dont get it
>搞不懂为什么 linux 每天都要更新
linux doesn't need to be updated if your machine just works.
如果你机器用着没问题,linux 根本不用更新。
been using Pikaur for years, shows you the diff on changes and I really like the version highlight
Pikaur 用了好几年了,会显示变更的 diff,而且我很喜欢版本高亮功能
reading this thread is pure ragebait, do niggers really not know how to compile their own software?
看这帖子纯属找气受,这些人真不知道咋自己编译软件吗?
HAHAHAHAHAHAHA AHAHAHAHAHAHAHAAH OPEN SOOOOOOOOOOOOOORES!!!!!!!!!!!
>>109451850
Compile it yourself, use the flatpak/appimage if available or use an APT distro and just get the .deb file
自己编译,或者有 flatpak/appimage 就用,要么换个 APT 系发行版直接拿 .deb 文件
>>109456649
How do you compile it yourself?
怎么自己编译?
Should I switch from AUR Google Chrome to the flatpak?
我应该从 AUR 的 Google Chrome 换成 flatpak 吗?
>>109456656
>Chrome
You can't compile that. Just use the flatpak.
那个编译不了的。直接用 flatpak 吧。
>>109444364
>>109445008
>How are you supposed to install things that aren't in pacman if the AUR isn't safe?
>如果 AUR 不安全,那 pacman 里没有的东西该怎么装?
By not using a DIY tinker distro with the sole purpose of tinkering. If you don't want, know or care how to build your own system from scratch then why are you using Arch? CachyOS is just Arch with a better installer (which already defeats the whole purpose of using Arch). Arch is meant to be a model kit that you assemble yourself.
别用这种纯粹为了折腾而存在的 DIY 折腾型发行版就行了。你不想、不会也不关心怎么从零搭自己的系统,那用 Arch 图啥?CachyOS 就是个装了个更好安装器的 Arch(这本身就违背了用 Arch 的全部意义)。Arch 就是一个给你自己拼装的模型套件。
Use a real distro that is meant to be used which actually has all the packages in it's main repo instead of a shitty user repo filled with malware. The reason the AUR exists in the first place is because the main Arch repos barely have any packages in them.
用个正经的、真正拿来用的发行版,主源里啥都有,而不是靠一个堆满恶意软件的用户仓库。AUR 存在的原因本身就因为 Arch 主源里压根没几个包。
>>109456672
What reason do I have to bother switching over to the flatpak if the AUR for it isn't compromised?
既然 AUR 里的包没被入侵,我有啥理由费劲换成 flatpak?
>>109456694
>Use a real distro that is meant to be used
>用个正经的、真正拿来用的发行版
such as?
比如?
I daily drove steamOS for years which is why I went with Cachy
我日常用 SteamOS 用了好几年,所以才选了 Cachy
>>109456705
Either Ubuntu or Fedora, everything else is just a meaningless reskin of those two anyway. Maybe Debian if you really hate Canonical for some reason and don't care about outdated packages. Choose the spin with the desktop environment you want and be done with it. Everything else is just a downgrade in terms of package availability. Use flatpaks, snaps or appimages for anything else.
要么 Ubuntu 要么 Fedora,其他都是这俩的白费功夫换皮。除非你特别恨 Canonical 又不在乎包老旧,那可以选 Debian。挑个带你要的桌面环境的版本就完事了。其他的在软件包可用性上都是降级。其他的用 flatpak、snap 或 appimage 解决。
The reason SteamOS uses Arch as a base is because Valve can freeze the packages at any time they want and not be dependent on the release cycle of another distro. But as a user this doesn't matter in any way. ChromeOS uses Gentoo as a base for similar reasons and no cares about it as well.
SteamOS 用 Arch 做底是因为 Valve 想啥时候冻结包版本都行,不用依赖别的发行版的发布周期。但这对普通用户来说毫无意义。ChromeOS 也因类似原因用 Gentoo 做底,也没人在乎。
>literally do anything except learning how to read the PKGBUILD
>让他干点啥都行就是不肯学怎么读 PKGBUILD
Why are zoomers like this?
为什么Z世代(Zoomers)都这样?
>>109445897
Every piece of open source software can get hacked too and it happened before. One developer gets his credentials stolen and the hacker pushes malware in a commit without anyone realizing. Or the hacker puts some backdoor into the software with a PR without anyone realizing. Or maybe the software was compromised from the very beginning and no one ever checked the source code.
每一款开源软件也同样可能被黑,这种事以前就发生过。某个开发者的账号被盗,黑客在提交里塞了恶意代码,谁也没察觉。或者黑客通过PR往软件里埋了后门,照样没人发现。再或者,软件从一开始就被动了手脚,而根本没人检查过源代码。
It's a bit scary to think about how fragile this whole system is. Ideally you would use a minimal amount of software made by a large group with lots of eyes on it that get paid for their work and only install it from the developers themselves and not rely on third party packaging. But the repo system of Linux doesn't allow this.
想想这整套系统有多脆弱,真有点吓人。理想情况下,你应该尽量少装软件,只用大团队开发、盯着看的人多、而且拿工资干活的那种,安装时也从开发者自己手里拿,别依赖第三方打包。但Linux的软件仓库机制根本不允许这么干。
>>109456753
>never seen a pkgbuild in my life
>这辈子没见过pkgbuild长啥样
>ask chatgpt
>直接问ChatGPT
I ain't reading all that mumbo jumbo shit nerd
我才懒得看你那堆天书一样的废话好吧,书呆子
>>109456900
Saar
>>109419858
Why not just use pacman as your main and nix package manager as your secondary? And there's also flatpak and appimages. You don't even need the AUR at all. Why do anons like to hurt themselves? :(
为什么不干脆用pacman当主力,Nix包管理器当备胎?另外还有flatpak和appimages可以用啊。你根本用不着碰AUR。为啥匿名版老哥非要自己折磨自己呢?:(
>>109456748
but I'm already familiar with arch
可我已经用惯Arch了
I don't want to switch
我不想换系统
>>109456994
I've never even heard of nix
Nix这玩意儿我听都没听过
can I use it on Arch
能在Arch上用吗
there's stuff I wanted to use that's only in the AUR
有些工具我想要的,只有AUR里才有
>>109456900
>use nerd distro for nerds
>用了个给极客准备的极客发行版
>be surprised about nerd shit inside his nerd distro
>结果被发行版里的极客玩意儿吓到了
When will people finally understand that the sole purpose of Arch is too read meaningless junk like this because nerds enjoy it? The whole install process is about reading some badly written wiki that tells you what commands you need to copy and paste and reading up on the fine details of bootloaders and other nonsense. I can't fathom how it got popular in the first place.
什么时候人们才能明白,Arch存在的唯一意义就是让人读这种毫无意义的废话,因为极客们就喜欢这个?整个安装过程就是读一遍写得稀烂的wiki,告诉你该复制粘贴哪些命令,再去研究引导加载器的各种细节和别的乱七八糟的东西。我实在想不通它当初是怎么火起来的。
>>109457039
Yes you can use Nix on Arch, but isn't Nix also user run?
对,你可以在Arch上用Nix,但Nix不也是用户自己跑的吗?
>>109457018
>but I'm already familiar with arch
>可我已经用惯Arch了
In what way? Every distro functions the same since they all use the exact same software stack with the exception of the package manager. The only difference you will notice is that you have a system that actually works with way more software available.
哪方面用惯了?所有发行版功能上都一样,因为底层软件栈完全相同,唯一的区别就是包管理器。你唯一能感觉到的差别是,换完之后系统真能好好干活了,而且能用的软件多了去。
>>109456695
You're the one asking what to use instead of the AUR, but to answer your question I would never consider installing software from something as fundamentally flawed as the AUR, but that's your decision to make.
是你在问有什么能替代AUR,但回答你的问题:我绝对不会考虑从AUR这种从根上就满是毛病的地方装软件,但那是你自己要做的决定。
>>109456748
This echoes my own opinion. I've played with Arch in a VM many times, but I'd never install it on my machine. Personally I use Debian, but I've previously used Ubuntu and Fedora.
这话说到我心坎里了。我在虚拟机上玩过好几次Arch,但绝不会装到自己机器上。个人用的Debian,之前也用过Ubuntu和Fedora。
>>109457065
I don't want to have to relarn all the terminal nomenclature
我不想重新背一堆终端命令术语
>>109456830
isnt debian sid worse than arch?
Debian Sid难道不是比Arch还不靠谱吗?
its the devlopment branch and they dont gurantee security
那是开发分支,他们不保证安全性
>>109457048
Nix:
Changes require a Pull Request (PR) on GitHub.
代码变更需要在GitHub上提交拉取请求(PR)。
PRs are reviewed by multiple maintainers who specialize in that area.
PR会由多名专门负责那一块的维护者审查。
A PR can take days or weeks to be merged.
一个PR可能要等好几天甚至几周才会被合入。
Every PR submitted to nixpkgs is automatically tested by Hydra, a massive, automated build farm.
提交到nixpkgs的每个PR都会由Hydra自动测试,那是一个大型自动化构建农场。
The package is built in an isolated sandbox on Nix's build farm.
这个包是在Nix构建农场的隔离沙箱里编译的。
The sandbox has no network access and cannot read your home folder.
沙箱没有网络访问权限,也读不到你的主目录。
Each package has one or more designated maintainers who keep an eye on it.
每个包都有至少一个指定的维护者盯着。
So NIx has safety measures while the AUR doesn't. I just vibeposted this so take that for what you will.
所以Nix有安全措施,而AUR没有。我就是随口这么一说,信不信随你。
>>109457092
You wouldn't need to use the terminal in the first place if you would just use one of those two distros and I doubt there is anything else you need the terminal for. On Arch based distros you need to install packages through the terminal because pacman doesn't integrate into KDE Discover for example. All other terminal commands are the same since they all use the same command line tools.
你要是用那两个发行版之一,根本不用碰终端,我怀疑你也没别的需要终端的事。Arch系发行版你只能用终端装包,比如pacman没法集成到KDE Discover里。其他终端命令都一样,反正用的都是同一套命令行工具。
apt and dnf are also way more sensible in their naming like "apt uninstall firefox" instead of "pacman -Rns firefox".
apt和dnf的命名也更合理,比如“apt uninstall firefox”比“pacman -Rns firefox”清楚多了。
>>109457209
well I've gotten somewhat used to using the terminal because I like being able to see exactly what's happening and knowing exactly what I'm doing
嗯,我倒是有点习惯用终端了,因为我喜欢能看到每一步在干嘛,心里有数。
I've already gotten comfortable with CachyOS on my new PC and don't want to fucking start start all over again
我在新电脑上已经习惯了CachyOS,不想他妈从头再来一遍。
>>109457154
>its the devlopment branch
>这是开发分支
True
>and they dont gurantee security
>而且他们不保证安全性
Security updates aren't guaranteed to be timely. I would not run it on servers. But for example Firefox is updated very quickly, almost always faster than Fedora.
安全更新不保证及时。我不会在服务器上跑这个。但比如Firefox更新特别快,几乎总是比Fedora还快。
>>109457247
Nta, you'll have to at some point unless you go with an established distro. Meme distros like cachy come and go
扯淡,你迟早得换,除非你用一个稳定的发行版。像Cachy这种梗发行版来去匆匆。
>>109427143
>No, it's because it's inherently more secure than Microsoft operating systems.
>不,那是因为它天生就比微软操作系统更安全。 ⁾ 几十年前大家就知道了,Linux之所以“天生更安全”,只是因为用的人太少,攻击它纯属浪费时间。OSX也一样,直到在大学里火起来使用量暴涨,才招来一波恶意软件狂潮。
Its been known for decades that Linux is only "inherently safer" through usage being so low that targeting them was a waste of time. OSX was the same way, until usage spiked due to being popular in universities and colleges which brought an onslaught of malware.
几十年来大家都知道,Linux所谓“天生更安全”不过是因为用的人太少,攻击它纯属浪费时间。OSX也一样,直到它在大学和学院里火起来,使用量暴涨,结果招来了一大波恶意软件。
>You think servers aren't also targets of viruses?
>你觉得服务器就不是病毒目标了?
The vast majority of server attacks are done without any malware at all, and Linux servers still do get attacked.
大多数服务器攻击根本不用恶意软件,而且Linux服务器确实也会被攻击。
>>109457302
>meme distros
>梗发行版
what is with retards and attaching meaningless buzzwords to shit they don't like
这些傻逼怎么老爱往自己看不惯的东西上贴无意义的新词
shut the fuck up
闭嘴吧
Isn’t the main problem with AUR that, when you use it, you should always check the pkgbuild and not just go ahead and install it straight away?
AUR的主要问题不就是,用它的时候得先查pkgbuild,不能直接装了就走吗?
>>109457325
>Its been known for decades that Linux is only "inherently safer" through usage being so low that targeting them was a waste of time.
>几十年前大家就知道了,Linux之所以“天生更安全”,只是因为用的人太少,攻击它纯属浪费时间。
Simply incorrect.
这纯粹是错的。
>>109457335
https://en.wikipedia.org/wiki/Category:Discontinued_Linux_distributions
95%+ of distros end up this list. Cachy will be one of them.
95%以上的发行版最后都会进这个名单。Cachy也会是其中之一。
>>109457337
Yes, anyone who has even the slightest knowledge about Linux or computers in general knows that you are required to always check the pkgbuild and you should only use the AUR if absolutely necessary. But every single Linux shill always talks about how amazing the AUR is and how it is this magically wonderland that will solve all your problems which is why people start using it without understanding what it is. I can't even blame them since you would expect those supposedly smart Linux users to know what they are talking about and not spout ridiculous lies.
是的,任何对Linux或电脑稍有了解的人都知道,你必须总是检查pkgbuild,而且只有在绝对必要时才应该使用AUR。但每个Linux吹子都在喋喋不休地吹捧AUR有多神奇,说它是什么能解决你所有问题的魔法仙境,这就是为什么人们会在不了解它是什么的情况下开始使用它。我甚至不能怪他们,因为你本来会指望那些自称聪明的Linux用户知道自己在说什么,而不是满嘴跑火车地扯谎。
Basically all the Linux shilling is build on lies and overexaggeration which is why so many people think that Linux is immune to malware and viruses like here >>109427143 and then they turn off their brain and start doing dumb shit with their computer like running random code from a random guy on the internet. I'm not sure if Linux users lie on purpose or if they are just clueless. Windows is so much more secure than desktop Linux that it isn't even comparable.
基本上,所有吹Linux的话都是建立在谎言和夸张上的,这就是为什么这么多人认为Linux对恶意软件和病毒免疫,就像 >>109427143 这里说的那样,然后他们脑子一热,就开始干蠢事,比如运行网上某个陌生人写的随机代码。我不确定Linux用户是故意撒谎还是他们本身就一无所知。Windows比桌面Linux安全太多了,根本没法比。
>>109457584
Pointing out that desktop Linux is more secure than Windows (which is objectively true) is not claiming that it's immune to malware and viruses. Resorting to strawman arguments just makes your own position look bad.
指出桌面Linux比Windows更安全(这是客观事实)并不是说它对恶意软件和病毒免疫。拿稻草人谬误来抬杠只会让你自己的立场看起来很糟。
LALALA NOT LISTENING
FUCK YOU AUR.
FUCK YOU ARCH, AND THE HORSE YOU RODE IN ON.
>>109457335
Every few years there is a new Arch based distro that gets shilled and then quickly forgotten. Manjaro, EndeavourOS, Garuda are all irrelevant now and you would even get mocked for being stupid enough to fall for it nowadays by the nice Linux community. All those distros are just reskins of Arch that add a functioning installer to it and preinstall Steam so that they can call themselves a gaming distro. None of these distros add anything of value and are basically identical. One day the person making the distro will get bored and abandon it and then a new flavor of the year distro will take it's place.
每隔几年就有一个新的基于Arch的发行版被吹上天,然后很快就被遗忘。Manjaro、EndeavourOS、Garuda现在都过气了,你要是现在上当受骗,还会被那些“友善”的Linux社区嘲笑你蠢。这些发行版都只是Arch的换皮,加了个能用的安装器,预装Steam,好自称游戏发行版。这些发行版没有一个带来真正的价值,基本上一模一样。总有一天做这个发行版的人会腻了然后弃坑,然后一个新的一年一换的发行版就会接替它的位置。
>>109457716
I always considered Arch to be a somewhat of a midwit spiritual successor to Slackware or LFS
我一直觉得Arch算是Slackware或LFS的某种中庸精神续作。
>>109457739
EndeavourOS is basically flavored Archinstall. I don't see any downside to using that over Arch or vice versa. It's kind of a pointless distro, but that's not exactly a crime.
EndeavourOS基本上就是带味的Archinstall。我看不出用它和用Arch有什么区别,反过来也一样。这算是个没什么意义的发行版,但也不算罪过。
I use Arch and I don't have any malware installed it just works and it's still the best no frills simple distro, maybe if you are a baby or mentally defective you can use Ubuntu or Fedora that way you can dribble on your keyboard
我用Arch,我没装任何恶意软件,它就是这么好用,而且它仍然是最简单无花哨的发行版。也许你要是像个婴儿或者脑子有问题,你可以用Ubuntu或Fedora,那样你就能在键盘上流口水了。
>>109420941
Add more packages to the main arch repo reducing the need for aur
往主Arch仓库里多加点包,减少对AUR的需求。
>>109457862
you can swap to the cachyos repos easily with an existing arch setup, they include a lot of aur packages they build themselves
你可以轻松地把现有的Arch设置切换到cachyos的仓库,他们收录了很多他们自己编译的AUR包。
>>109457894
there's stuff that still isn't in there that I want to use
但还是有我想用的东西不在里面。
YOTLD AMIRITE GUISE?
>>109457894
I checked it and only one of my AUR packages is in it
我查了一下,我用的AUR包里只有一个是里面有的。
>>109457621
That post didn't claim it but I heard it before when the reality is just that the marketshare is too irrelevant. Servers and desktops have completely different attack vectors and can't be compared in any way. Servers have very minimal software installed and are constantly monitored and hardened to ensure security. Hacking a server means finding vulnerabilities in the software that they run which requires immense effort. But it is worth it for hackers since they can hold the company for ransom money and make millions.
那帖子没这么说,但我之前听说过,实际上市场份额太不值一提了。服务器和桌面电脑的攻击途径完全不同,根本无法相提并论。服务器装的软件极少,且持续监控和加固以保安全。攻击服务器得找它们运行软件里的漏洞,这需要极大的功夫。但对黑客来说值,因为可以勒索公司赎金,赚上百万。
On a Linux desktop you just have to give the user an infected program and you can steal all the info you want from their PC and they will never know. Something like this wouldn't happen on a server unless some very stupid person was involved.
在Linux桌面上,你只要给用户一个带毒的程序,就能偷走他们电脑上的所有信息,他们根本不会察觉。这种事在服务器上不会发生,除非有个特蠢的人掺和进来。
On Windows you would never install weird shit from third party repos like on Linux and Windows Defender alone does a better job blocking viruses than anything on Linux. On Linux you sometimes don't even have a firewall by default, no secureboot, no disk encryption by default like Bitlocker, no app monitoring that blocks suspicious activity, no Windows Hello to block access to your passwords, no UAC. Flatpak sandboxing even breaks the browsers internal sandboxing which makes it less secure. Windows is made for desktop security while on Linux you just rawdog everything.
在Windows上,你绝不会像在Linux那样从第三方仓库装怪东西,而且Windows Defender单独干就比Linux上任何杀毒方案都更能拦病毒。Linux有时连默认防火墙都没有,没有安全启动,没有像Bitlocker那样的默认磁盘加密,没有阻止可疑活动的应用监控,没有Windows Hello来保护你的密码,没有UAC。Flatpak的沙箱甚至破坏了浏览器内部的沙箱,这让它更不安全。Windows是专为桌面安全设计的,而在Linux上你就是裸奔式操作。
>>109457849
I will never understand how people can have this inflated sense of superiority just because they copy and pasted some commands from some wiki.
我永远搞不懂,就凭从wiki上复制粘贴了几条命令,怎么就能有这种膨胀的优越感。
>>109420941
Use multiple AI agents to review and flag any suspicious changes.
用多个AI代理来审查并标记任何可疑更改。
If the package is flagged then the user is warned about the potential security problem and for the package to be unflagged it will need to go through a manual review process done by potentially multiple trusted maintainers.
如果包被标记了,用户就会收到潜在安全问题的警告,而要取消标记,就得经过可能多位可信维护者的手动审查流程。
>>109458309
Clearly copying and pasting commands from the wiki isn't working because tourists are having a mental breakdown over malware in the AUR. Maybe you shouldn't be using Arch if you do that.
显然从wiki复制粘贴命令并不管用,因为那些“游客”在AUR里看到恶意软件就崩溃了。你要这样干,就别用Arch了。
>>109458511
If people didn't have this retarded sense of superiority just because they run a specific OS and talk about it all the time then they wouldn't attract midwits that want to larp as intellectuals. They even go so low as to use the arch install script or use a preconfigured Arch distro just so they can say "I use Arch btw" even though that defeats the whole purpose of it. No other distro has this retarded cult mentality not even Gentoo.
如果人们不因为跑特定操作系统就在那里吹个不停、整天炫耀的话,就不会招来那些想装高知的半吊子。他们甚至堕落到用Arch安装脚本或预配置的Arch发行版,就为了说“顺便说一句我用Arch”,尽管这完全违背了它的初衷。没有其他发行版有这种傻逼邪教心态,连Gentoo都没有。
>>109458573
Gentoo users do have it. Mostly toward Arch users though. Because it's "harder" to set up Gentoo compared to Arch. (although it's not actually hard to set up either)
Gentoo用户确实有这毛病,主要是冲着Arch用户去的。因为跟Arch比,装Gentoo“更难”。(虽然实际上也不难装)
>>109419858
On Debian, so *shrug*
在Debian上,所以*耸肩*
(如果你觉得这篇文章有启发,可以点击这里付费)